
What Is a Security Architect?
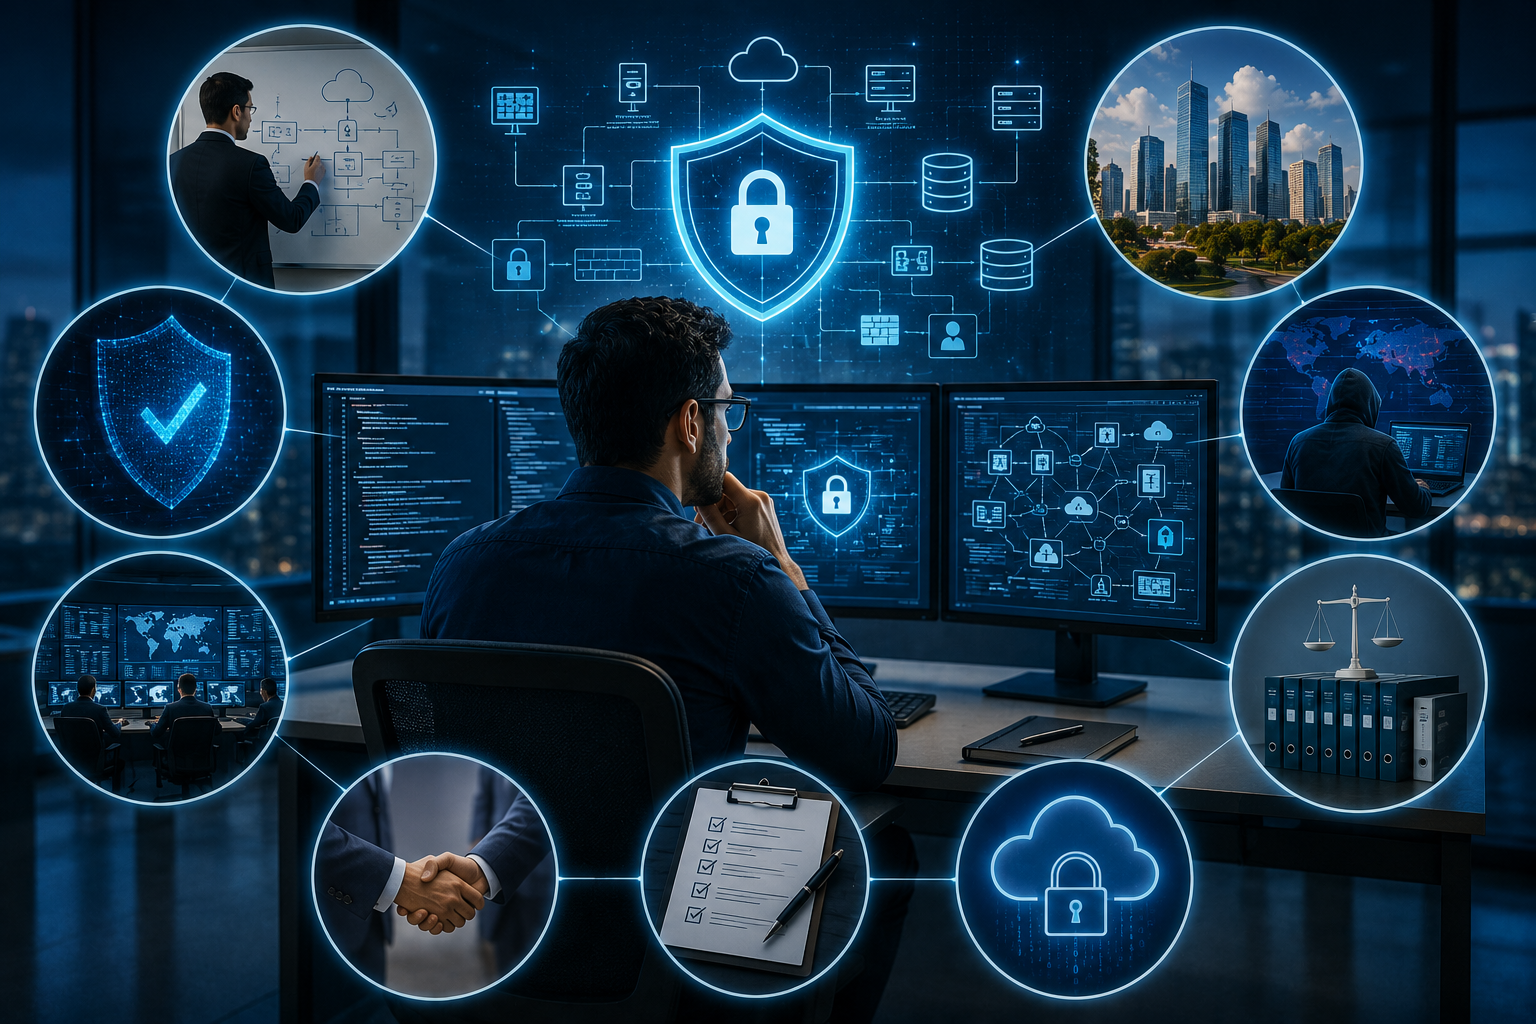
A Security Architect designs how an organization’s technology should be protected before it’s built, not after. Where most cybersecurity roles react to problems — patching vulnerabilities, investigating alerts, responding to incidents — a Security Architect works upstream, deciding how networks, applications, cloud environments, and identity systems should be structured so fewer problems occur in the first place.
In simple terms: if a company is building a new customer portal or cloud environment, the Security Architect answers “how do we build this so it’s defensible, not just functional?”
More technically: a Security Architect designs, documents, and governs the security structure of an organization’s IT systems — networks, applications, cloud infrastructure, identity, and data — applying security principles and controls in a way that aligns with business risk tolerance and regulatory obligations.
That last part matters. Security architecture isn’t just about picking strong controls; it’s about picking the right controls for the organization’s actual risk profile, budget, and operational reality. A control appropriate for a bank is often wildly excessive for a five-person startup.
Where the Role Fits Within Cybersecurity
Analysts monitor for threats. Engineers implement and maintain security tools. Penetration testers try to break things. Incident responders clean up afterward. The Security Architect sits at a different point in that lifecycle: design — working closely with enterprise architects, security engineers, developers and DevOps teams, risk and compliance teams, and executive leadership.
Why Organizations Need Security Architects
Security added after the fact is expensive and usually resented by the teams retrofitting it. A cloud environment built without segmentation is far harder to secure six months after go-live than it would have been to design correctly from day one. Security Architects exist to prevent that pattern — their value is measured in problems that never happened because the underlying design didn’t allow them.
Security Architecture vs General Cybersecurity
“Cybersecurity” is the umbrella term for protecting systems, networks, and data. “Security architecture” is a specific discipline within it — designing systems with security built into their structure. A general practice might be “encrypt sensitive data”; architecture asks the harder questions underneath — where encryption should happen, who manages the keys, what happens if a key is compromised, and how the decision interacts with every other system touching that data.
What Does a Security Architect Do?
Responsibilities are broad and vary by organization size and maturity. In smaller companies, one person covers most of these areas; in large enterprises, architects often specialize — cloud, application, network, or identity architecture.
Designing Security Architecture
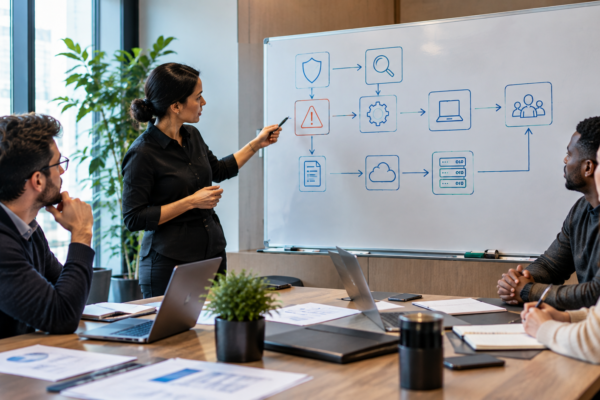
At the core, this means producing architecture diagrams, reference designs, and technical standards that describe how systems should be built securely — a target-state network diagram, a cloud landing zone design, or a set of application security patterns development teams are expected to follow.
Identifying Security Risks and Threat Modeling
Architects assess proposed and existing environments to find where risk is concentrated — an exposed database, an overly permissive IAM role, a third-party integration with excessive access. This is structural risk analysis, often done through design review rather than automated tools alone. Threat modeling is the architect’s most distinctive activity: systematically asking who might attack a system, how, and what they’d gain — often using a framework like STRIDE (Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, Elevation of Privilege).
Security Requirements
Translating abstract security goals into concrete, testable requirements is a core skill. “The system must be secure” is not a requirement. “All API endpoints must enforce authentication via OAuth 2.0 with short-lived tokens, and administrative endpoints must additionally require MFA” is.
Network and Cloud Security Design
Even in cloud-heavy organizations, network security design remains relevant — segmentation, zoning, traffic filtering, and secure connectivity between on-premises and cloud environments. Increasingly this extends to designing identity, networking, logging, and workload security within AWS, Azure, or Google Cloud, often across more than one simultaneously.
Application Security and Identity and Access Management
Working with development teams so applications are designed with authentication, authorization, input validation, and secure data handling built in from the start. IAM design — how users, services, and systems authenticate and what they’re permitted to do — is one of the highest-leverage areas an architect touches, since IAM mistakes are a common root cause of real-world breaches.
Zero Trust Architecture
Designing systems around the principle that no user or device should be implicitly trusted regardless of network location — verifying identity, device posture, and context continuously rather than once at the perimeter.
Data Protection and Security Controls
Deciding how sensitive data is classified, where it can live, how it’s encrypted, and how access is controlled and audited — then selecting the actual technical and administrative controls (firewalls, encryption standards, logging, access controls) that implement it.
Compliance, Governance, and Security Reviews
Mapping architecture decisions to regulatory and framework requirements (ISO/IEC 27001, PCI DSS, industry-specific rules), maintaining documentation that shows how the environment meets them, and reviewing new projects and vendor integrations before they go live to catch architectural risk early.
Incident Preparedness
Architects don’t typically run incident response, but they design for resilience and recoverability — segmentation that limits blast radius, logging that supports investigation, and backup architecture that supports recovery.
In a real organization, these responsibilities rarely happen in isolation. A single cloud migration might require network design, IAM design, data protection decisions, and compliance mapping all at once — interdependent, and needing to be explained to people who don’t share the architect’s technical background.
A Day in the Life of a Security Architect
There’s no single “typical day,” but most days share a similar shape: a mix of meetings, design work, documentation, and reactive requests. A realistic week might include:
- Architecture review meetings — evaluating whether a proposed system meets security requirements and flagging what needs to change before approval.
- Threat modeling sessions — working through a new feature with developers and product owners to identify what could go wrong.
- Cloud architecture discussions — reviewing a proposed landing zone, questioning IAM role design, checking logging and segmentation against standards.
- Application design reviews — going through API designs, auth flows, and data handling with engineering teams.
- Risk analysis and documentation — writing architecture decision records and standards documents; less glamorous than it sounds, and it takes up more time than most people expect.
- Working with developers and infrastructure teams — finding a pragmatic middle ground on implementing a requirement without blowing a sprint deadline, and coordinating on network or cloud configuration changes.
- Working with executives — translating risk into business language, usually to justify budget or a decision to delay a launch.
- Reviewing security incidents — not running the response, but checking afterward whether an incident exposed an architecture gap that needs closing.
The honest version of this role involves a lot of context-switching and writing, and a constant need to defend decisions to people with competing priorities — a product manager who wants to ship faster, a developer who thinks a control is overkill. Communication consumes as much of the job as technical design does, sometimes more.
Security Architect vs Other Cybersecurity Roles
These role boundaries blur in smaller organizations, but understanding the intended distinctions helps clarify where a Security Architect fits.
Security Architect vs Security Engineer
The Security Architect designs; the Security Engineer builds and operates what’s designed. An architect might specify “all traffic between these two network zones must pass through a stateful firewall with these logging requirements”; the engineer configures the firewall and keeps it running. Architects work at a higher level of abstraction across more systems at once; engineers go deep on implementation and reliability.
Security Architect vs Security Analyst / SOC Analyst
SOC and Security Analysts typically work within a Security Operations Center, monitoring alerts and triaging incidents in real time — operational, day-to-day defensive work. A Security Architect operates on a longer time horizon, designing the systems that generate the signals analysts monitor, including the log sources and alerting thresholds that shape what the SOC watches.
Security Architect vs Incident Responder
Incident Responders handle the aftermath of an event: containment, eradication, recovery. Architects are involved before an incident, through design that reduces its chance and impact, and sometimes after, through post-incident review — but they aren’t typically the ones responding in real time.
Security Architect vs Penetration Tester
A Penetration Tester actively tries to break into systems, usually as a time-boxed engagement. An architect designs systems to make that job harder. In mature organizations, pen test findings feed back into architecture decisions — a recurring pattern usually points to a design gap, not just isolated misconfigurations.
Security Architect vs Security Consultant
A Security Consultant may do architecture work, but typically as an external advisor on a specific engagement without long-term ownership. A Security Architect is usually internal, with ongoing accountability for how systems evolve over time. Consultants add value for specialized expertise, but don’t carry the same continuity.
| Role | Primary Focus | Time Horizon | Typical Seniority |
|---|---|---|---|
| Security Architect | Designing secure systems | Long-term, ongoing | Senior |
| Security Engineer | Building and operating controls | Ongoing, operational | Mid to senior |
| Security Analyst / SOC Analyst | Monitoring and triage | Real-time | Entry to mid |
| Incident Responder | Containing and recovering from incidents | Real-time to short-term | Mid to senior |
| Penetration Tester | Finding exploitable weaknesses | Engagement-based | Mid to senior |
| Security Consultant | External advisory | Engagement-based | Varies |
Key Skills Every Security Architect Needs
Technical Skills
A Security Architect needs breadth more than any other role in cybersecurity, because architecture decisions touch nearly every layer of the technology stack.
- Networking — routing, segmentation, VPNs, and how traffic actually moves through an environment
- Operating systems — enough Windows and Linux depth to know where controls are enforced and where they can be bypassed
- Cloud platforms — hands-on familiarity with at least one major provider, increasingly more than one
- Identity and access management — how authentication and authorization work, including OAuth 2.0, SAML, and OpenID Connect
- Encryption — when and how to apply it at rest and in transit, and the operational realities of key management
- Application and API security — secure coding principles, common vulnerability classes, and how apps and APIs should authenticate, authorize, and handle data
- Database and endpoint security — access control and auditing at the data layer; how endpoint posture fits the broader architecture
- Network security — firewalls, segmentation, intrusion detection, secure connectivity patterns
- DevSecOps, containers, and Kubernetes — integrating security into CI/CD and securing containerized, orchestrated workloads
- Infrastructure as Code — reviewing and writing secure Terraform or CloudFormation templates, since misconfigured code becomes misconfigured production
- Security monitoring — knowing what needs to be logged and monitored, even without watching the dashboard directly
- Threat modeling and risk management — structured, repeatable risk analysis rather than a one-off exercise
Architecture Skills
Beyond individual technical domains, Security Architects need to think in systems and patterns:
- Designing secure systems from the ground up, rather than retrofitting controls onto existing designs
- Security-by-design and defense in depth — treating security as a design input, and layering controls so a single failure doesn’t cause full compromise
- Zero Trust and least privilege — designing around continuous verification and the minimum access necessary
- Segmentation — limiting how far an attacker can move after gaining a foothold
- Secure authentication and authorization design — getting identity right, since so much else depends on it
- Resilience and disaster recovery — designing systems that can withstand and recover from failure, not just prevent it
Business Skills
This is the area where technically excellent people most often fall short of architect-level performance. A Security Architect who can design a perfect Zero Trust network but can’t explain why it’s worth the budget and disruption to a skeptical VP of Engineering will struggle to get anything implemented.
- Communication and risk communication — explaining technical risk in terms non-technical stakeholders can act on, in a way that supports decisions rather than just raising alarms
- Stakeholder management — building trust with developers, infrastructure teams, and executives who have competing priorities
- Business understanding — knowing what the organization does, how it makes money, and what it can’t afford to lose
- Documentation and decision-making — writing decisions clearly enough for others to maintain years later, and making calls under uncertainty
- Leadership and budget awareness — influencing without always holding direct authority, and knowing that “more secure” isn’t automatically “better” if it’s disproportionate to the risk
A Security Architect who only understands technology will design systems that are secure but unworkable. A Security Architect who only understands business will design systems that are workable but insecure. The role exists at the intersection, and that’s what makes it hard to hire for — and valuable when done well.
Security Architecture Frameworks and Standards
Frameworks give Security Architects a shared vocabulary and starting structure, rather than requiring every organization to invent security architecture from scratch.
Zero Trust
An architectural approach, not a product: trust is never assumed by network location, and every access request is authenticated, authorized, and continuously validated.
NIST Cybersecurity Framework and Guidance
The CSF organizes activities around identify, protect, detect, respond, and recover, and is used less as a technical blueprint than a way to check coverage and find gaps. NIST also publishes deeper technical guidance, including material on Zero Trust and system security engineering, referenced when justifying specific design decisions.
CIS Controls
A prioritized set of defensive actions, useful as a practical baseline checklist rather than an abstract framework.
ISO/IEC 27001
An information security management standard widely used as the basis for governance and certification, especially in regulated industries.
SABSA
Built specifically for security architecture, insisting every design layer trace back to a business requirement. Less commonly implemented in full than NIST or ISO, but its business-driven philosophy shapes how experienced architects think regardless.
TOGAF Where Relevant
An enterprise architecture framework, not security-specific, but relevant wherever an organization uses enterprise architecture practices, so security isn’t treated as a disconnected discipline.
Defense in Depth
Less a formal framework than a principle: layering controls across network, endpoint, identity, application, and data so a single failure doesn’t cause full compromise.
Few organizations adopt any single framework wholesale. Most architects blend elements from several, adapted to size, risk tolerance, and regulatory obligations.
Tools and Technologies Security Architects Work With
Security Architects generally don’t operate tools day-to-day the way engineers or analysts do, but they need to understand these categories well enough to make informed design decisions and evaluate whether existing tooling actually supports the architecture.
- Cloud security platforms — visibility and policy enforcement across cloud environments, including posture management
- IAM solutions — identity providers and access management platforms implementing authentication and authorization design
- SIEM — centralized logging and correlation that architecture decisions need to feed properly
- EDR/XDR — endpoint-level visibility and response capability
- Firewalls and WAF — traditional and cloud-native network firewalls, plus application-level protection understood as a mitigating control, not a substitute for secure design
- Vulnerability management platforms — identifying weaknesses that feed into architectural risk decisions
- Secrets management — securely storing and rotating credentials, API keys, and certificates rather than leaving them hardcoded
- Encryption and key management tools — for data at rest and in transit
- API and container security tools — gateways for API traffic; scanning and runtime protection for containerized workloads
- DevSecOps tools — static and dynamic analysis integrated into CI/CD pipelines
- Architecture and documentation tools — diagramming and modeling tools used to produce and maintain architecture artifacts
The specific vendor matters far less than understanding what problem each category solves. Tool selection is usually an engineering decision made within the boundaries an architect sets, not the other way around.
Cloud Security Architecture
Cloud environments changed security architecture more than almost any other development in recent years, which is why it deserves its own section here. Security Architects working across AWS, Microsoft Azure, and Google Cloud need platform-specific fluency, since each provider’s identity model, networking constructs, and default security posture differ meaningfully — architecture that’s sound on AWS doesn’t translate directly to Azure without adaptation.
Key areas of focus include:
- Cloud IAM — more granular and more easily misconfigured than on-premises identity; getting this right is arguably the highest-impact decision in cloud architecture
- Network segmentation — virtual networks, subnets, and security groups designed with the same principles as physical networks, adapted to cloud-native constructs
- Cloud logging — knowing what’s logged by default versus what must be explicitly enabled
- Encryption and key management — deciding between provider-managed and customer-managed keys, and how key rotation and access are governed
- Secrets — ensuring credentials and API keys aren’t embedded in code, config files, or container images
- Workload security — securing compute resources, whether virtual machines, containers, or serverless functions
- Containers and serverless — secure image pipelines and runtime protections for containers; function permissions and event-source security for serverless
- Multi-cloud environments — consistent policy enforcement and visibility across more than one provider doesn’t happen automatically and adds real complexity
Traditional security architecture assumed a defensible network perimeter. Cloud architecture assumes there isn’t one — workloads are ephemeral, access is API-driven, and the “network” is often software-defined rather than physical. Architects who came up in traditional network security sometimes struggle with this shift, because “harden the perimeter” doesn’t map cleanly onto an environment where resources appear and disappear via API call.
Application Security Architecture
Working with development teams is one of the more demanding parts of the role, partly because it requires translating security requirements into language and workflows that fit how developers actually build software.
Secure SDLC and Threat Modeling
Security needs to be embedded across the development lifecycle — requirements, design, coding, testing, deployment, and maintenance — rather than appearing only as a pre-launch gate. Threat modeling is the architect’s core tool here: systematically identifying what could go wrong in a design before it’s built.
Authentication, Authorization, and API Security
Getting identity right at the design stage prevents entire categories of vulnerabilities. Poorly designed authorization logic — where a user can access another user’s data by changing an ID in a URL — remains one of the most common real-world flaws despite being well understood for years. Since modern applications are built as collections of APIs, securing each one (authentication, rate limiting, input validation, proper error handling) is central to the discipline.
Input Validation and Secrets Management
Never trust input from outside the system boundary — whether from a user, another service, or a third party. Applications also need credentials to talk to databases and other services; architecture must specify how those secrets are stored, accessed, and rotated, not hardcoded into source code.
Dependency Risks and Secure Coding
Modern applications rely heavily on open-source libraries, introducing supply-chain risk that architecture needs to account for through vetting and monitoring. Architects don’t typically write production code, but need enough secure coding fluency for credible conversations with developers.
DevSecOps, CI/CD Security, and Testing
Integrating security checks into the CI/CD pipeline means feedback happens early and continuously rather than as a late-stage gate. The pipeline itself needs its own security architecture — access controls, secrets handling, build artifact integrity — alongside static analysis, dynamic analysis, and dependency scanning.
Security designed in from the start is cheaper and far less disruptive than security added after a system is already built. A vulnerability found in design review costs a conversation; the same vulnerability found in production can cost an incident.
Zero Trust and Modern Security Architecture
Zero Trust deserves a dedicated section because it represents a genuine shift in how security architecture is approached, not just a rebranding of older ideas. The traditional model assumed that anything inside the corporate network could be trusted, and security’s primary job was defending the perimeter — firewalls at the edge, VPNs for remote access, relatively open trust once “inside.” That model breaks down when employees work from anywhere and applications live in the cloud.
Zero Trust replaces that assumption with continuous verification: no user, device, or service is trusted by default, regardless of network location. Key principles include identity-centric security (identity, not location, is the basis for access decisions), least privilege, continuous verification (trust evaluated repeatedly, not just at login), device trust, microsegmentation (small, tightly controlled network zones that limit an attacker’s movement), and application-aware access scoped to specific resources rather than broad segments.
A practical example: under a traditional model, an employee on VPN might gain broad internal network access. Under Zero Trust, that employee authenticates to a specific application, device posture is checked, and access is scoped narrowly to what that application requires, with no implicit trust extended elsewhere.
Zero Trust isn’t a product an organization buys, despite how it’s often marketed — it’s an architectural approach that typically takes years to implement fully, usually starting with identity before extending into network and application layers.
How to Become a Security Architect
Security Architect is a senior role — it’s not realistic to move directly into this position from an entry-level background or a single certification. Most Security Architects have somewhere between seven and fifteen years of broader IT and security experience before stepping into the role, though this varies.
Stage 1–3: IT, Networking, and Systems Foundations
Start with how operating systems and applications work, then build networking knowledge — routing, subnetting, firewalls, how traffic actually flows. Get hands-on with server administration, virtualization, and at least one major cloud platform. This foundation matters more than it seems early on, since later architecture decisions depend on genuinely understanding system behavior.
Stage 4–5: Enter Security and Gain Hands-On Experience
Move into a security-specific role — SOC analyst, security analyst, or junior security engineer — then spend real time on vulnerability management, incident response exposure, or compliance work. This is where pattern recognition develops: an intuitive sense for where risk concentrates.
Stage 6–7: Engineering and Architecture Skills
Security engineering — building and implementing controls — develops the practical depth architecture decisions need to be grounded in reality; many architects spend years engineering first. From there, start taking on design responsibilities before holding the title — contributing to reviews, documenting standards, leading a project’s security design.
Stage 8: Move Toward Security Architect
By this stage the transition is often about demonstrated capability more than a formal process — many people grow into the role internally, or move externally once they can point to real architecture work they’ve led. There isn’t one path through these stages; people enter and exit in different orders depending on background.
Education and Qualifications
A bachelor’s degree in computer science, information technology, cybersecurity, or a related field is common among Security Architects, and many postings list one as a preference. That said, it’s not universally mandatory — demonstrated skill, experience, and relevant certifications can compensate at many organizations, particularly for candidates with a strong track record.
Relevant technical experience matters more than the specific degree title. A computer science graduate, a networking-focused IT graduate, and a self-taught engineer with a decade of hands-on experience can all reach architect-level roles by different paths, built on the same underlying requirement: deep, demonstrated technical competence combined with sound judgment.
Degree requirements vary by employer, industry, and country. Highly regulated industries and large enterprises are more likely to treat a degree as a hard requirement; smaller companies are often more flexible if a candidate can demonstrate equivalent skill.
Security Architect Certifications
Certifications can demonstrate structured knowledge and commitment to the field, but they don’t replace hands-on experience, and no certification guarantees employment.
- CISSP — a broad, senior-level ISC2 certification commonly held by Security Architects and often listed as preferred or required, covering a wide range of security domains rather than deep technical specialization.
- SABSA-related credentials — tied to the SABSA framework, useful for formalizing architecture-specific methodology, though less universally required than CISSP.
- CCSP — also from ISC2, focused on cloud security, increasingly relevant given how central cloud has become to the role.
- Security+ — an entry-level certification, useful as an early foundation rather than a senior-stage primary credential.
- Cloud and vendor-specific certifications — provider security specialty credentials that demonstrate platform-specific depth, useful where an organization is heavily invested in a particular ecosystem.
Earlier-career certifications demonstrate foundational knowledge; mid-career, platform-specific ones demonstrate practical depth; senior, broad certifications like CISSP tend to matter most once someone already operates at a senior level. None substitute for the judgment that comes from actually designing and defending real architecture decisions — hiring managers for architect-level roles weigh demonstrated experience far more heavily than certification lists.
Security Architect Salary
Security Architect compensation varies substantially and depends on several interacting factors:
- Country and city — cost of living and local tech salary norms create large regional differences
- Experience level — a newly promoted architect and one with fifteen years of experience aren’t paid the same
- Industry — regulated industries like finance and healthcare often pay a premium given compliance stakes
- Company size, cloud expertise, certifications, and leadership responsibility — larger enterprises, deep cloud skills, credentials like CISSP, and team-leading responsibility all shift compensation
One global figure would be misleading. Check current data from national labor statistics agencies or reputable salary aggregators that state their methodology, for your specific country, city, and experience level, rather than relying on a number that may already be outdated.
Career Progression
There isn’t one canonical path into this role. A few common patterns:
- Security Analyst → Security Engineer → Senior Security Engineer → Security Architect — the most traditional route, building operational experience into engineering depth before design.
- Network Engineer → Security Engineer → Senior Security Engineer → Security Architect — common for people bringing strong infrastructure fundamentals into architecture work.
- Software Engineer → Application Security → Security Architect — increasingly common as developers move into security and specialize in application security architecture.
- Cloud Engineer → Cloud Security Engineer → Security Architect — a newer but increasingly common path, reflecting how central cloud has become to architecture.
These paths aren’t identical for everyone, and people often combine elements of more than one. What matters more than the sequence is accumulating broad technical depth and genuine design experience along the way.
What Makes a Great Security Architect?
Technical skill alone doesn’t make someone architect-level. The qualities that separate a strong Security Architect from a technically skilled engineer include:
- Systems thinking and curiosity — seeing how a change in one part of an environment affects others, and a genuine interest in how things actually work
- Risk awareness — an intuitive sense for where risk concentrates, developed through experience rather than a checklist
- Business understanding — knowing what the organization values and can’t afford to lose
- Communication and simplifying complexity — making technical risk understandable to people who don’t share the technical background
- Technical depth — enough hands-on credibility that engineers and developers trust the guidance
- Strategic thinking — designing for where the organization is heading, not just where it is today
- Documentation and leadership — writing decisions clearly enough to remain maintainable years later, and influencing outcomes without always holding direct authority
The difference between technically skilled and architect-level often comes down to judgment under ambiguity. A skilled engineer implements a well-defined control correctly. An architect decides which controls are worth implementing at all, given imperfect information, competing priorities, and a budget that never quite matches the ideal design.
Common Mistakes Aspiring Security Architects Make
- Chasing certifications without experience — certifications support a resume but don’t substitute for real design experience.
- Learning tools without fundamentals — configuring a product matters less than understanding the principle behind it; tools change, fundamentals don’t.
- Ignoring business requirements or usability — an elegant design that ignores budget, timeline, or usability gets rejected or worked around, often creating worse risk than the original problem.
- Tunnel vision on one domain — network-only focus, or ignoring cloud or application security, leaves real blind spots.
- Poor documentation — a design that exists only in someone’s head isn’t architecture, it’s a preference.
- Overengineering — controls added because they’re theoretically ideal, not proportionate to actual risk, waste budget and erode trust.
- Treating compliance as security — passing an audit and being genuinely secure are related but not identical.
- Designing security nobody can operate — an architecture that outstrips the organization’s staffing or expertise will fail in practice, however sound it looks on paper.
Skills to Learn in 2026
Some of these areas are well-established best practices; others are still maturing, and it’s worth being honest about that distinction rather than presenting everything as equally settled.
Established priorities: cloud security (now core, not emerging), identity security (growing more central as Zero Trust adoption increases), Zero Trust itself (increasingly the default architectural approach, though full implementation remains a multi-year effort), API and application security (mainstream skills, overlapping with DevSecOps), supply-chain security (standard practice following a run of high-profile industry incidents), container security, and Infrastructure as Code security.
Emerging, actively developing areas: AI security — securing systems with AI/ML components, including model access, data exposure, and output validation — and AI-assisted cybersecurity, using AI tools to support architecture review and threat modeling. Both are worth building early familiarity with, but the space is still developing rapidly, and today’s specific practices may shift as the technology and associated risks mature further.
Security Architect Career Roadmap for Beginners
This roadmap assumes someone starting from a general IT background aiming toward architecture over several years — not someone with zero technical background aiming to reach architecture in months, which isn’t realistic.
0–3 months — Build foundational IT knowledge: operating systems, basic networking, how systems communicate. If already working in IT, deepen your understanding of the systems you touch daily.
3–6 months — Get hands-on with a cloud platform through a free tier or lab. Learn core security concepts — CIA triad, authentication vs authorization, common vulnerability classes. Consider Security+ if aiming for a first security role.
6–12 months — Find an entry point into security specifically — SOC analyst, junior security engineer, or an IT role with security responsibilities. Follow how real vulnerabilities and incidents are reported publicly, to build pattern recognition.
1–2 years — Deepen hands-on skill in a specific area — cloud, application, or network security. Start participating in security reviews or threat modeling if your role gives you exposure, even informally.
2–4 years — Move into security engineering if you haven’t already, and take on design-adjacent responsibilities — documenting standards, leading a project’s security portion, mentoring juniors. This is typically where “doing security tasks” starts shifting to “designing security systems.”
Beyond four years, the path becomes more individual, but the throughline stays the same: accumulate real, hands-on experience across multiple domains before expecting to move into architecture.
Practical Projects for Aspiring Security Architects
- Designing a Zero Trust architecture — Design remote and internal application access for a small organization under Zero Trust principles; document the reasoning versus a traditional perimeter approach. Demonstrates identity-centric architecture thinking.
- Designing a secure cloud environment — Build a segmented landing zone in a free-tier AWS, Azure, or GCP account with proper IAM, logging, and encryption. Demonstrates hands-on cloud security architecture.
- Building a secure web application architecture — Design auth, authorization, data handling, and API security for a simple app, backed by a threat model. Demonstrates application security architecture in a concrete context.
- Designing IAM policies — Build least-privilege roles for a hypothetical set of users and services, documenting the reasoning behind each permission. Demonstrates one of the highest-value skills in the role.
- Creating a network segmentation architecture — Design a zoned network for a hypothetical organization with documented rationale for each boundary. Demonstrates foundational architecture, still relevant in cloud-heavy environments.
- Threat modeling a SaaS application — Produce a full STRIDE-based threat model of a real or hypothetical SaaS product, including a data flow diagram and mitigations. Demonstrates structured, repeatable threat modeling.
- Designing a secure CI/CD pipeline — Design a pipeline with checks integrated throughout — static analysis, secrets management, build integrity — documenting why each control sits where it does. Demonstrates DevSecOps architecture.
- Creating a security architecture document — Write a formal architecture document for any project above, as if it needed real organizational review. Demonstrates the documentation skill underpinning the entire role.
Frequently Asked Questions
What is a Security Architect? A senior cybersecurity professional who designs how an organization’s networks, applications, cloud environments, and data should be structured to be secure, based on its specific risk profile.
What does a Security Architect do? Designs security architecture, performs threat modeling, defines security requirements, reviews new systems before launch, and translates business risk into technical controls across networking, cloud, applications, and identity.
Is Security Architect a senior role? Yes — it typically requires several years of broad technical and security experience first.
How do I become a Security Architect? By building a foundation in IT and networking, moving into security-specific roles, gaining hands-on engineering experience, and progressively taking on design responsibility over several years.
Do Security Architects need coding skills? Not necessarily at a professional developer level, but understanding how code works and common vulnerability patterns matters for credible conversations with developers.
Which certifications are useful? CISSP is widely recognized for senior security roles; cloud-specific certifications (CCSP or provider-specific credentials) are increasingly valuable given how central cloud has become.
Is CISSP useful for Security Architects? Yes — it’s one of the most commonly held certifications in the role, though it matters most as a complement to real experience, not a substitute.
What is the difference between Security Architect and Security Engineer? Architects design; engineers build and operate what’s designed. Architecture is higher-level and longer-horizon; engineering is more hands-on and operational.
How long does it take to become a Security Architect? No fixed timeline, but most people reach the role after roughly seven to fifteen years of combined IT and security experience.
What skills are most important? Broad technical knowledge (networking, cloud, identity, applications), architecture-specific thinking (defense in depth, least privilege, Zero Trust), and business communication skills.
Can a software engineer become a Security Architect? Yes — software engineers who move into application security often bring coding and system-design experience that translates well into architecture work.
Can someone become a Security Architect without a degree? It’s possible with strong hands-on experience and relevant certifications, though larger or more regulated employers often list a degree as preferred or required.

Leave a Reply