

Introduction — Why Networking Is a Core Cybersecurity Skill
An analyst opens an alert: an internal host has made repeated outbound connections to an unfamiliar IP address on an unusual port, every sixty seconds, for the last four hours. The SIEM flagged it. Now someone has to actually explain what it means — is that IP a CDN, a misconfigured backup job, or a compromised machine beaconing to a command-and-control server? Answering that question requires networking knowledge, not a security product license.
This is the pattern behind almost every meaningful security event. Malware communicates over a network. Attackers move laterally across a network. Data gets exfiltrated across a network. Even purely endpoint-based compromises eventually touch the network somewhere — a callback, a download, a lateral connection. A security professional who doesn’t understand how networks actually work can read an alert’s headline but not its substance, which means they can escalate or panic but can’t genuinely investigate.
Networking fundamentals for cybersecurity aren’t a separate, optional specialization — they’re the connective tissue running underneath SOC monitoring, penetration testing, incident response, cloud security, and security engineering alike. A SOC analyst reads a firewall log; that log means nothing without understanding ports and protocols. A penetration tester enumerates a target; that process is entirely networking-driven. An incident responder builds a timeline of lateral movement; that timeline is a network story. This guide walks through the networking concepts that actually matter for this work, connected the whole way through to what security professionals do with them, not treated as a standalone networking course.
What Is Computer Networking?
At its core, networking is the set of rules and infrastructure that let separate computers exchange data reliably.
What Happens When One Computer Communicates With Another?
When one computer sends data to another, the data gets broken into smaller units, addressed with source and destination information, passed through a series of intermediate devices (switches, routers), and reassembled at the destination. Each step in that journey — addressing, routing, delivery, reassembly — is a place where something can go wrong, get misconfigured, or get deliberately abused, which is exactly why understanding the journey matters for security work.
LAN, WAN, Internet, and Enterprise Networks
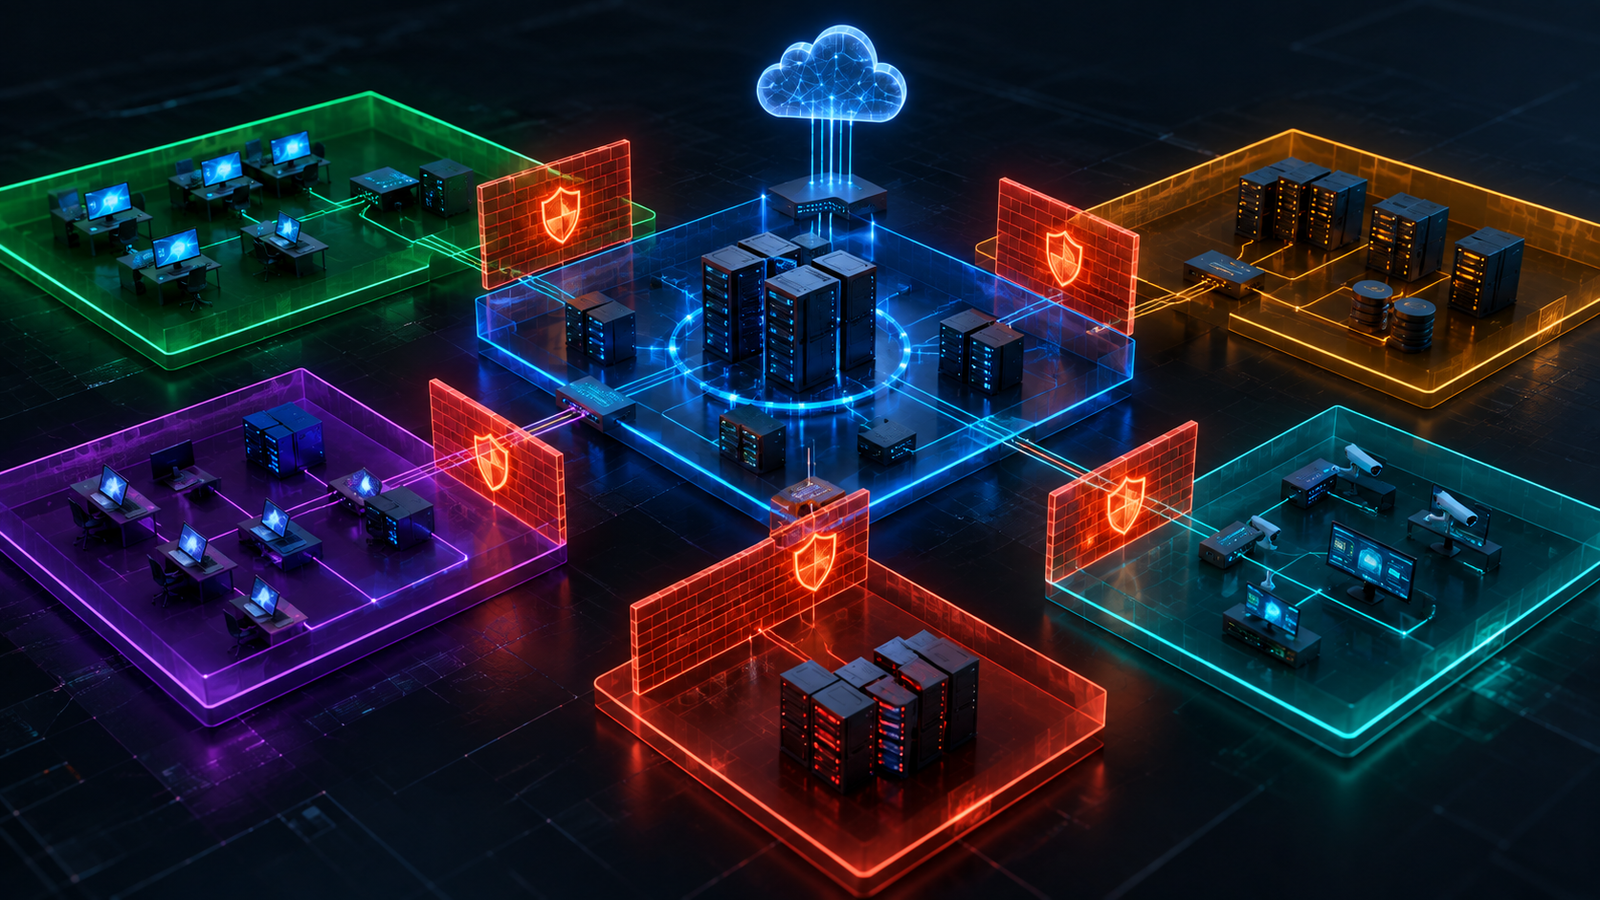
A LAN (Local Area Network) connects devices within a limited physical area — an office, a home, a single building. A WAN (Wide Area Network) connects networks across larger distances, often linking multiple offices or a company’s data centers together. The internet is the largest WAN of all — a global network of networks. Enterprise networks typically combine several LANs, WAN connections between sites, and increasingly a mix of on-premises and cloud infrastructure, usually segmented into zones with different trust levels. Security professionals need to understand this structure because attacks — and defenses — behave differently depending on which of these boundaries traffic is crossing.
Client, Server, and Peer-to-Peer Communication
Most enterprise traffic follows a client-server model — a client (a browser, an application) requests something, and a server responds. Peer-to-peer communication, where systems talk directly without a central server, is less common in typical enterprise environments but shows up in some collaboration tools and, notably, in some malware communication patterns designed to avoid a single point of detection. Recognizing which model a given piece of traffic follows is often the first step in deciding whether it looks normal.
The OSI Model and TCP/IP Model
These models sound academic, but they’re genuinely practical: they give security professionals a shared vocabulary for describing exactly where in the communication process something is happening — which matters enormously when troubleshooting, analyzing packets, or writing up an investigation.
The Seven OSI Layers
- Physical — the actual transmission medium: cables, radio signals, electrical signals. Security relevance: physical access control, cable tapping risk, and wireless signal interception.
- Data Link — handles communication between devices on the same local network, using MAC addresses. Security relevance: ARP spoofing and switch-based attacks happen at this layer.
- Network — handles addressing and routing between different networks, primarily through IP. Security relevance: IP spoofing, routing manipulation, and most firewall filtering decisions happen here.
- Transport — manages end-to-end communication reliability, primarily through TCP and UDP. Security relevance: port scanning, connection state tracking, and most intrusion detection signatures operate at this layer.
- Session — manages and maintains the connection between two systems over time. Security relevance: session hijacking and session fixation attacks target this layer’s concepts.
- Presentation — handles data formatting, encryption, and compression. Security relevance: TLS encryption formally operates near this layer.
- Application — the layer users and applications directly interact with, including HTTP, DNS, and SSH. Security relevance: the overwhelming majority of security tooling and web-facing attacks operate here.
TCP/IP Model
The practical model most real-world networking documentation actually uses collapses the OSI layers into four: Network Access (physical and data link combined), Internet (routing and addressing), Transport (TCP/UDP), and Application (everything above transport, combined into one layer).
OSI vs TCP/IP
| OSI Model | TCP/IP Model |
|---|---|
| Physical, Data Link | Network Access |
| Network | Internet |
| Transport | Transport |
| Session, Presentation, Application | Application |
These models matter during troubleshooting (narrowing down exactly which layer a problem sits at — is DNS failing, or is the connection itself unreachable?), packet analysis (describing precisely what a packet capture shows), incident response (explaining an attack’s technical mechanics clearly in a report), and network security investigations generally, where precise layer-based language avoids the ambiguity of describing something as just “not working.”
IP Addresses — The Foundation of Network Communication
An IP address is a numeric identifier assigned to a device on a network, used to route traffic to and from that device. IPv4 addresses use a 32-bit format written as four numbers separated by dots (192.168.1.10), giving roughly 4.3 billion possible addresses — a number the internet has already outgrown, which is part of why IPv6 exists.
Static IP addresses stay fixed and are commonly used for servers and infrastructure that other systems need to reliably find. Dynamic IP addresses are assigned automatically, typically through DHCP, and can change over time. The loopback address (127.0.0.1, referred to as localhost) always refers to the local machine itself, used constantly for local testing. The network address identifies the network itself (not a usable host), and the broadcast address sends traffic to every device on a given network segment at once.
Private IP Address Ranges
Private IP ranges (10.0.0.0/8, 172.16.0.0/12, 192.168.0.0/16) are reserved for internal use and aren’t routable directly on the public internet. Enterprise networks use private addressing internally for nearly every device, translating to a public address only at the network’s edge. Understanding these ranges instantly tells an analyst whether traffic they’re looking at originated inside or outside the organization’s own network — a distinction that matters in almost every investigation.
Public IP Addresses
Public IP addresses are globally unique and routable across the internet — anything internet-facing (a web server, a mail gateway, a VPN endpoint) needs one. Security implications follow directly: anything with a public IP is reachable by anyone on the internet by default, which makes public-facing systems the natural starting point for both attackers and authorized penetration testers during reconnaissance.
IPv6 for Cybersecurity
IPv6 uses a much larger 128-bit address space, and adoption continues growing steadily, particularly in cloud and mobile networks. It’s a genuine mistake for a security professional to ignore it — a network that’s carefully monitored on IPv4 but has IPv6 quietly enabled and unmonitored has a real blind spot, since traffic can traverse a network over IPv6 without appearing in IPv4-focused logging or filtering at all.
Subnetting and CIDR for Cybersecurity
A subnet is a logically segmented portion of a larger network. The subnet mask defines which part of an IP address identifies the network and which part identifies the specific host. CIDR (Classless Inter-Domain Routing) notation expresses this compactly — 192.168.1.0/24 means the first 24 bits identify the network, leaving the remaining 8 bits for host addresses (254 usable addresses on that particular subnet).
A simple way to think about it: in 192.168.1.0/24, everything from 192.168.1.1 through 192.168.1.254 sits on the same local subnet, while 192.168.2.x sits on a different one — meaning traffic between them has to pass through a router, which is exactly where a firewall rule can be applied.
Why Cybersecurity Professionals Need Subnetting
Subnetting underpins network segmentation — deliberately separating sensitive systems (databases, domain controllers) from general user traffic so that a compromise in one segment doesn’t automatically reach the other. It’s the basis for firewall rules, which are frequently written in terms of entire subnets rather than individual addresses. It informs access control decisions about which segments can reach which. During incident investigation, recognizing which subnet a compromised host sits on immediately narrows down what else it could plausibly reach. It supports asset identification, since knowing an organization’s subnet layout tells an analyst what should and shouldn’t exist on a given segment. And it carries directly into cloud networking, where virtual networks are subnetted using exactly the same CIDR logic.
MAC Addresses, ARP, and the Data Link Layer
A MAC address is a hardware-level identifier burned into a network interface, used for communication within a local network segment (as opposed to IP addresses, which handle routing between networks). Ethernet is the dominant standard for wired local networking, using MAC addresses to deliver frames to the correct device on a shared segment.
ARP (Address Resolution Protocol) maps IP addresses to MAC addresses on a local network — when a device wants to send traffic to an IP address on its own subnet, it uses ARP to find the corresponding MAC address. Devices maintain a temporary ARP cache of these mappings to avoid repeating the lookup for every packet.
Why ARP Matters in Cybersecurity
ARP spoofing (or ARP poisoning) is a local-network attack where a malicious device sends forged ARP replies, tricking other devices into sending traffic to the attacker instead of the legitimate destination — a classic technique for intercepting local traffic. Because ARP operates with essentially no built-in authentication, it’s inherently vulnerable to this kind of manipulation. Defensively, this connects to network visibility — monitoring for unexpected or rapidly changing ARP entries is a genuine detection opportunity, and switch-level protections (like dynamic ARP inspection) exist specifically to reduce this risk. This is worth understanding at the conceptual, defensive level: recognizing the pattern in monitoring, not executing it against a network without authorization.
TCP and UDP — Understanding Transport Protocols
TCP
TCP (Transmission Control Protocol) is connection-oriented — it establishes a formal connection before sending data. It’s reliable, guaranteeing that data arrives, arrives in order, and is re-sent if lost. This relies on sequencing (numbering data so it can be reassembled correctly), acknowledgments (confirming receipt), and retransmission (resending anything that doesn’t get acknowledged). Every TCP connection begins with a three-way handshake — SYN, SYN-ACK, ACK — which is exactly the exchange a packet capture shows at the start of any TCP session, and exactly what an incomplete handshake in a capture can reveal about a failed or blocked connection attempt.
UDP
UDP (User Datagram Protocol) is connectionless — it sends data without establishing a session first, with no guarantee of delivery or order. This gives it much lower overhead, making it the natural choice for latency-sensitive traffic like DNS lookups, video streaming, and VoIP, where a dropped packet matters less than speed. Security-wise, UDP’s lack of a handshake makes source addresses easier to spoof, which is part of why UDP-based protocols are commonly abused in reflection and amplification-style denial-of-service attacks.
TCP vs UDP
| TCP | UDP | |
|---|---|---|
| Connection | Connection-oriented | Connectionless |
| Reliability | Guaranteed delivery | No guarantee |
| Speed | Slower (more overhead) | Faster (less overhead) |
| Common uses | Web browsing, email, file transfer | DNS, streaming, VoIP |
| Security note | Handshake enables session tracking | Easier to spoof source address |
For security monitoring, this distinction matters directly — TCP’s stateful nature makes tracking a connection’s full lifecycle straightforward, while UDP’s stateless nature means detection tools have to work harder to correlate related traffic without a formal session to anchor to.
Ports and Protocols Every Cybersecurity Beginner Should Know
A port is a numbered endpoint on a device that identifies a specific service or application — a single IP address can run many services simultaneously, distinguished by their port numbers.
Common services worth genuine familiarity with: HTTP (port 80, unencrypted web traffic), HTTPS (port 443, encrypted web traffic), SSH (port 22, encrypted remote administration), DNS (port 53, name resolution), DHCP (ports 67/68, automatic address assignment), FTP (ports 20/21, file transfer, largely legacy and unencrypted), SMTP (port 25, outbound mail), IMAP (port 143 or 993 encrypted, mail retrieval), RDP (port 3389, Windows remote desktop — a frequent target for brute-force and ransomware access), SMB (port 445, Windows file sharing, historically involved in major worm outbreaks), LDAP (port 389, directory services), and Kerberos (port 88, authentication, central to Active Directory environments).
Memorizing this list is far less useful than understanding the combination that actually matters: service + protocol + port + traffic behavior. A connection on port 443 that isn’t actually carrying TLS-encrypted HTTP traffic is a real anomaly worth investigating — the port number alone tells you what’s expected, not what’s actually happening.
Well-Known Ports vs Ephemeral Ports
Well-known ports (0–1023) are reserved for standard services, consistently assigned across systems (port 443 is always expected to be HTTPS, for example). Ephemeral ports are temporary, high-numbered ports (typically in the 32768–65535 range or similar, depending on the OS) that a client’s operating system assigns automatically for the outgoing side of a connection — this is why a packet capture of your own web browsing shows a normal server port like 443 on one side and a seemingly random high port on your own machine on the other.
Why Open Ports Matter to Security Professionals
Open ports define an organization’s attack surface — every listening service is a potential entry point. Asset discovery relies heavily on identifying what’s actually running and reachable, since undocumented services are a common security gap. Service identification during an investigation or authorized assessment tells a defender or tester exactly what they’re dealing with. Network monitoring watches for unexpected new listening ports as a possible sign of compromise or unauthorized software. And routine security auditing regularly reviews which ports are open against what’s actually supposed to be running, closing anything unnecessary.
DNS — The Internet’s Naming System
DNS (Domain Name System) translates human-readable domain names into the IP addresses computers actually use to communicate. A DNS resolution typically involves a recursive query — a client asks a resolver, which queries authoritative servers on the client’s behalf until it finds the answer, then caches it for future requests.
Common DNS record types: A records map a domain to an IPv4 address, AAAA records map to an IPv6 address, CNAME records alias one domain name to another, MX records specify mail servers for a domain, TXT records hold arbitrary text data (often used for domain verification and email authentication like SPF), and NS records specify a domain’s authoritative name servers.
Why DNS Matters in Cybersecurity
DNS is one of the richest sources of investigative signal available to a defender. Domain investigation — checking when a domain was registered, who it resolves to, and its reputation — is a routine part of triaging a suspicious connection. Threat intelligence feeds heavily rely on known-malicious domains as indicators. Malware very commonly uses DNS for command-and-control communication, since DNS traffic is almost always allowed outbound by default, making it an appealing channel for attackers to hide in. Suspicious domains — newly registered, using unusual character patterns, or mimicking a legitimate brand — are a standard early warning sign. DNS monitoring — watching query volume, destinations, and patterns — catches a meaningful share of compromise activity that other controls miss entirely.
DNS Security Concepts
DNS spoofing involves providing a false DNS response to redirect a victim to an unintended (often malicious) destination. DNS tunneling encodes non-DNS data inside DNS queries and responses, used defensively to describe how attackers can exfiltrate data or maintain command-and-control through a channel that often escapes scrutiny. DNS poisoning corrupts a resolver’s cache with false information, affecting every subsequent lookup that relies on that cache. Secure DNS concepts like DNSSEC add cryptographic validation to DNS responses, helping prevent exactly this kind of tampering. These are described here at a conceptual, defensive level — the value for a security professional is recognizing the pattern in monitoring, not executing it.
DHCP and Automatic Network Configuration
DHCP (Dynamic Host Configuration Protocol) automatically assigns IP addresses and network configuration to devices joining a network, removing the need for manual configuration on every device. A DHCP client (the joining device) requests an address from a DHCP server, which assigns one from a defined pool for a limited lease period, along with related configuration like the default gateway and DNS servers to use.
A rogue DHCP server — an unauthorized device on the network handing out its own configuration — is a genuine, conceptually important security concern: it could redirect victims’ DNS or gateway settings to attacker-controlled infrastructure, silently rerouting their traffic. Defenders watch for unexpected DHCP servers appearing on a network as a specific, well-understood red flag.
Routing and Default Gateways
Routing is the process of forwarding traffic between different networks. Routers make these forwarding decisions based on a routing table, which maps destination networks to the next hop needed to reach them. The default gateway is the router a device sends traffic to whenever the destination isn’t on its own local subnet — effectively the exit point from a local network toward everything else. Static routing configures routes manually; dynamic routing uses protocols that let routers automatically learn and adjust to changes in the network.
Why Routing Knowledge Matters in Cybersecurity
Routing knowledge underpins network segmentation design (deciding what can route to what, and where a firewall needs to sit to control it), understanding actual traffic paths (an investigation often needs to reconstruct exactly how traffic got from point A to point B), firewall placement decisions (a firewall is only effective sitting at a point traffic is actually forced to pass through), incident investigation (tracing lateral movement across network segments), cloud infrastructure (virtual networks rely on the same routing concepts, implemented through the provider’s own tooling), and general network architecture review during security assessments.
NAT and Network Address Translation
NAT (Network Address Translation) translates private IP addresses used inside a network into a public IP address for communication with the outside internet, and translates responses back to the correct internal device. This is how an entire office of devices using private addressing can all share a single public IP address for outbound internet access.
Organizations use NAT primarily for practical reasons — extending the usable life of scarce public IPv4 addresses and keeping internal addressing simpler to manage — rather than purely as a security measure. It’s worth being direct about a common misconception: NAT provides a byproduct of obscuring internal addressing from the outside, but it is not a firewall and not a complete security control on its own. A network relying on NAT alone, with no actual firewall policy behind it, still has meaningful exposure.
Firewalls and Network Security Controls
A firewall controls traffic based on defined rules, deciding what’s allowed to pass and what’s blocked. Packet filtering firewalls make decisions based on individual packet headers (source, destination, port). Stateful inspection firewalls track the state of active connections, making smarter decisions based on whether traffic is part of an established, legitimate session. Application-aware (or next-generation) firewalls go further, inspecting traffic content to identify the actual application in use regardless of the port it’s running on.
Firewall rules generally define inbound traffic (coming into a network) separately from outbound traffic (leaving it), and follow either an allow policy (blocking everything except what’s explicitly permitted — the more secure default) or a deny policy in reverse. Network segmentation, discussed earlier under subnetting, is frequently implemented and enforced through firewall rules placed between network zones.
Host-Based vs Network Firewalls
A network firewall sits at a network boundary, controlling traffic for every device behind it. A host-based firewall runs on an individual device, controlling traffic specifically to and from that machine — useful as a second layer of defense even inside an otherwise trusted network segment, since it protects a device even if something else on the same segment is compromised.
Why Firewall Rules Matter During Incident Response
During an investigation, reviewing firewall logs for blocked traffic can reveal attack attempts that never actually succeeded, which is still valuable intelligence. Unexpected allowed traffic — a connection that should have been blocked but wasn’t — often points directly to the misconfiguration that let an incident happen in the first place. Suspicious outbound connections allowed by an overly permissive rule are a common path for data exfiltration or command-and-control. And identifying specific policy violations — traffic that technically matched a rule but shouldn’t have been allowed under the organization’s actual intent — is a routine part of post-incident review and hardening.
VPNs and Secure Network Communication
A VPN (Virtual Private Network) creates an encrypted tunnel between two points over an otherwise untrusted network, protecting the confidentiality of the traffic inside it. A remote access VPN lets an individual user connect securely into an organization’s network from an untrusted location, typically requiring authentication before the tunnel is established. A site-to-site VPN connects two entire networks — two office locations, or an on-premises network and a cloud environment — over the internet as if they were directly connected.
Tunneling is the underlying mechanism: original traffic gets encapsulated inside an encrypted outer layer for its journey, then unwrapped at the other end. It’s worth being precise about what a VPN actually does and doesn’t do: it encrypts traffic in transit and can mask a user’s apparent network origin, but it does not make someone anonymous in any absolute sense, and it does not automatically make an endpoint secure — a compromised device sending traffic through a VPN is still a compromised device, just with an encrypted tunnel around its traffic.
HTTP and HTTPS for Cybersecurity
HTTP (Hypertext Transfer Protocol) structures web communication as requests (a client asking for something, using a method like GET or POST) and responses (the server’s reply, including a status code indicating success, redirection, or error). Headers carry metadata about the request or response. Cookies let a server store small pieces of data on the client, commonly used to maintain sessions — the mechanism that keeps a user “logged in” across multiple requests.
HTTPS wraps HTTP traffic in TLS (Transport Layer Security) encryption, protecting the confidentiality and integrity of the data in transit and providing some assurance about the server’s identity through certificates.
Why Web Traffic Knowledge Matters
Web traffic fluency matters directly for SOC monitoring (recognizing normal versus abnormal request patterns), web application security (understanding how the underlying protocol actually works is the foundation for spotting flaws in how an application implements it), threat detection (unusual headers, methods, or request patterns are often the earliest signal of an attack against a web application), incident response (reconstructing exactly what a web-based attack actually did from request and response logs), and penetration testing (web-facing applications are consistently among the most common entry points tested in an authorized engagement).
Network Traffic and Packets
A packet is the basic unit of data traveling across a network, containing a source and destination address, the protocol in use, relevant ports, a payload (the actual data being carried), and various headers describing how to handle it along the way. Packet capture tools record this raw traffic for later, detailed analysis.
What Security Professionals Look for in Network Traffic
Analysts watch for unusual destinations (traffic to an IP or domain that doesn’t fit the organization’s normal pattern), unexpected ports (a service running somewhere it shouldn’t be, or traffic on a port that doesn’t match its expected protocol), repeated connections at suspiciously regular intervals, beacon-like behavior (a classic sign of malware checking in with a command-and-control server on a fixed schedule), large data transfers that could indicate exfiltration, protocol anomalies (traffic that claims to be one protocol but doesn’t actually behave like it), and generally unexpected outbound traffic that doesn’t match the organization’s known, legitimate patterns. This kind of pattern recognition is squarely defensive — the goal is spotting what shouldn’t be there, not a guide to disguising traffic to avoid exactly this kind of detection.
Network Monitoring and Traffic Analysis
Visibility is the precondition for detection — an organization can’t investigate what it never observed in the first place. Network monitoring watches traffic and infrastructure continuously. Flow data (such as NetFlow) summarizes conversations between hosts — who talked to whom, how much data, over what protocol — without capturing full packet content, making it lightweight enough to retain at scale. Packet capture records the actual raw traffic, offering far more detail but at a much higher storage cost. Logs record events generated by individual systems and devices. Alerts fire when monitored activity matches a defined detection rule. Baselines establish what normal traffic looks like for a given environment, which is what makes an anomaly actually stand out as unusual rather than just different.
The distinction between these data types matters practically: packet capture gives full content detail but is expensive to retain long-term; network flow gives lightweight summary data suitable for long-term retention and broad pattern detection; network logs come from individual devices and applications describing their own activity; and SIEM data aggregates and correlates all of the above (plus much more) into a single searchable platform, which is exactly where a SOC analyst spends most of an investigation.
Essential Networking Commands for Cybersecurity
ping— tests basic reachability to a host and reports round-trip time. Security use: a fast first check of whether a host is even responding before deeper investigation.ip addr— displays a system’s network interfaces and assigned IP addresses. Security use: confirming exactly what address and interface configuration a host actually has during an investigation.ip route— displays the routing table. Security use: understanding exactly how a system would reach a given destination, useful when something isn’t routing as expected.ss— shows active sockets and listening ports on a system. Security use: identifying exactly what’s listening and what connections are currently active (ss -tulnpis a fast way to see every listening service and its owning process).traceroute— shows the path (hop by hop) traffic takes to reach a destination. Security use: understanding a connection’s actual route, useful when diagnosing unexpected routing or latency.dig/nslookup— perform DNS lookups. Security use: checking exactly what a domain currently resolves to, and comparing that against expected or historical values during a domain investigation.curl/wget— make HTTP requests from the command line. Security use: testing a web service’s response directly, or safely retrieving a file for offline analysis.tcpdump— captures live network traffic directly from the command line. Security use: a lightweight, always-available packet capture tool for quick, targeted traffic analysis during an investigation, even without a full GUI tool installed.
The value of this command set isn’t memorizing every flag — it’s the ability to quickly answer “what is this host actually doing on the network right now” without waiting on a heavier tool.
Essential Network Security Tools
- Wireshark — a graphical packet analysis tool for deep, detailed inspection of captured traffic, widely used for both learning and real investigation work.
- tcpdump — the command-line packet capture tool covered above, often used to capture traffic that gets analyzed later in Wireshark.
- Nmap — a network scanning tool used for host discovery, port scanning, and service identification, foundational to both defensive asset inventory and authorized penetration testing enumeration. Nmap’s scripting capabilities extend this further, allowing more detailed service and vulnerability checks — always within an authorized scope.
- Zeek — a network security monitoring tool that analyzes traffic and generates rich, structured logs describing network activity, widely used in security operations for detection and investigation.
- Suricata — an intrusion detection and prevention system that inspects network traffic against defined rules to flag or block known malicious patterns.
- Netcat — a flexible networking utility for testing connections, transferring data, and general network troubleshooting.
Every tool in this list assumes an authorized lab, an owned system, or a properly scoped security engagement — none of them are appropriate to point at infrastructure you don’t have explicit permission to test.
Networking for SOC Analysts
A SOC analyst investigating a network-related alert routinely checks the source and destination IPs involved (internal, external, known-good, or unfamiliar), reviews the ports in use against what’s expected for that service, checks recent DNS activity for the host involved, investigates outbound connections for anything unusual, applies protocol knowledge to judge whether traffic actually matches what it claims to be, reads network-based alerts in the context of the broader environment rather than in isolation, and correlates network events with endpoint logs to build a fuller picture of what actually happened. As ValuFlash’s detailed look at what SOC Analysts actually do day to day covers, this kind of methodical network and log correlation makes up a large share of genuine SOC work — networking fluency is what turns a raw alert into something an analyst can actually explain and act on.
Networking for Penetration Testers
Within an authorized, scoped engagement, networking knowledge drives most of a penetration tester’s early work: network discovery identifies what’s actually reachable, port and service enumeration reveals what’s running and how it might be vulnerable, understanding network segmentation informs how far a foothold could realistically spread, traffic analysis helps validate findings, and service identification narrows down exactly which vulnerabilities are worth pursuing. Testers also need to understand the difference between internal and external assessments — testing from outside the network entirely versus testing from an assumed foothold already inside — since the two produce very different findings. ValuFlash’s complete guide to becoming a penetration tester covers this progression in depth, and consistently points to networking fundamentals as one of the earliest and most important building blocks in the field.
Networking for Incident Responders
During an active investigation, responders rely on networking knowledge to identify suspicious connections, recognize command-and-control indicators in traffic patterns, spot signs of data transfer consistent with exfiltration, trace lateral movement indicators as an attacker (or a simulated one, in a lab) moves between systems, catch DNS anomalies tied to malicious infrastructure, investigate unexpected remote access, and construct an accurate network timeline of what happened and when. None of this evidence stands alone — correlating network evidence with endpoint and identity data is what actually turns isolated signals into a defensible conclusion. ValuFlash’s guide to building a career in incident response walks through this full investigative lifecycle, much of which is fundamentally a networking story from start to finish.
Networking for Cloud Security
Traditional networking concepts translate directly into cloud environments, just implemented through a provider’s specific tooling rather than physical hardware. Virtual networks are the cloud equivalent of a physical LAN. Subnets work exactly as they do on-premises, just defined through a console or Infrastructure as Code. Security groups and network ACLs function as cloud-native firewalls, controlling traffic at the instance or subnet level respectively. Routing determines how traffic moves between cloud subnets and out to the internet. Load balancers distribute traffic across multiple backend instances. Private endpoints let cloud resources communicate without ever traversing the public internet. Internet gateways provide the actual path in and out of a cloud network. Cloud firewalls apply the same allow/deny logic as their on-premises counterparts, adapted to a dynamic, API-driven environment.
The critical point: cloud security absolutely does not reduce the networking knowledge required — if anything, it demands the same fundamentals applied faster and more precisely, since cloud environments change constantly and a misconfigured security group can expose a resource to the entire internet in seconds. ValuFlash’s guide to the Cloud Security Engineer career path makes this point directly: strong traditional networking fundamentals are exactly what let someone reason clearly about cloud network design rather than just clicking through a provider’s console without understanding what each setting actually does.
Common Networking Mistakes Cybersecurity Beginners Make
- Memorizing port numbers without understanding the protocols and services behind them, which falls apart the moment something doesn’t match the memorized list.
- Skipping subnetting because it feels mathematically intimidating, then struggling to reason about segmentation and firewall rules later.
- Ignoring DNS, missing one of the richest and most accessible sources of investigative signal available.
- Not genuinely understanding TCP/IP, leading to surface-level pattern matching instead of real comprehension.
- Learning tools before networking fundamentals, producing someone who can run Wireshark but can’t explain what the capture actually shows.
- Confusing IP addresses with MAC addresses, which leads to real confusion during local-network investigations.
- Assuming HTTPS automatically means an application is secure, when it only guarantees the transport layer is encrypted — the application itself can still be badly built.
- Treating a VPN as a complete security solution rather than one specific control addressing one specific risk.
- Ignoring outbound traffic while focusing entirely on inbound threats, missing exfiltration and command-and-control activity that moves the other direction.
- Skipping packet analysis entirely because it looks intimidating, losing one of the most direct ways to actually verify what’s happening on a network.
How Much Networking Do You Actually Need for Cybersecurity?
| Role | Required Networking Depth |
|---|---|
| SOC Analyst | Solid — ports, protocols, DNS, basic packet reading |
| Security Analyst | Solid — similar to SOC, plus broader risk context |
| Incident Responder | Deep — full traffic analysis and timeline reconstruction |
| Penetration Tester | Deep — enumeration and exploitation depend on it directly |
| Security Engineer | Deep — designing and maintaining network controls |
| Cloud Security Engineer | Deep — cloud networking builds directly on these fundamentals |
| Security Architect | Very deep — architecture decisions span the whole network |
| DevSecOps Engineer | Moderate to solid — enough to secure CI/CD and infrastructure traffic |
The specific depth varies, but there’s no cybersecurity role on this list where networking knowledge is genuinely optional — the difference is how deep the requirement goes, not whether it exists at all.
Practical Networking Labs for Cybersecurity Beginners
- Build a small virtual network using a hypervisor and a couple of virtual machines.
- Identify your own machine’s local IP configuration with
ip addr. - Examine your own routing table with
ip routeand understand every entry in it. - Resolve DNS records for a few domains using
dig, and compare A, MX, and TXT records. - Observe active TCP connections on your own machine using
ss. - Capture traffic in an authorized lab environment using
tcpdump, then review it in Wireshark. - Analyze a publicly available, legally distributed sample PCAP file for practice.
- Configure a basic firewall (like
ufworiptables) on a personal Linux VM. - Create simple network segmentation between two virtual machines and test connectivity between them.
- Practice subnetting calculations on paper until the math becomes fast and intuitive.
- Investigate sample or synthetic network logs and practice identifying what looks unusual.
Only analyze or test networks and systems you own or have explicit authorization to access.
Networking Learning Roadmap for Cybersecurity
Stage 1 — Networking Basics
Understand how devices communicate, and the difference between a LAN, a WAN, and the internet.
Stage 2 — IP Addressing and Subnetting
Comfortably read and calculate basic subnets and CIDR notation.
Stage 3 — TCP/IP and Protocols
Understand TCP versus UDP, and the common ports and protocols covered earlier.
Stage 4 — DNS, DHCP, and Routing
Understand how names resolve, how addresses get assigned, and how traffic actually gets routed.
Stage 5 — Firewalls and VPNs
Understand how traffic gets filtered and how encrypted tunnels protect it in transit.
Stage 6 — Packet Analysis
Get comfortable capturing and reading real traffic in Wireshark or tcpdump.
Stage 7 — Network Security Tools
Gain hands-on familiarity with Nmap, Zeek, and Suricata in an authorized lab.
Stage 8 — Realistic Security Labs
Apply everything learned so far to a full, simulated investigation scenario.
Certifications vs Practical Networking Skills
Networking and cybersecurity certifications can genuinely help structure early learning and get a resume past an initial screening, particularly with little prior experience to point to. But hands-on labs, real packet analysis experience, and documented portfolio projects consistently matter more as a career progresses. Networking-specific certifications and broader cybersecurity certifications both have value — but no single credential is mandatory, and none substitutes for the ability to actually read a packet capture or reason through an unfamiliar network problem under real conditions.
What Networking Skills Should You Put on a Cybersecurity Resume?
Vague claims like “networking — advanced” don’t tell an employer much. Specific, demonstrable skills carry more weight:
- TCP/IP fundamentals
- IPv4/IPv6 addressing
- Subnetting and CIDR
- DNS investigation and record analysis
- DHCP fundamentals
- Routing concepts
- Firewall rule design and review
- VPN configuration concepts
- Packet analysis with Wireshark
- Network monitoring and flow analysis
- Network troubleshooting
A documented project — a home lab writeup, an annotated PCAP analysis, a segmentation design applied to a personal environment — demonstrates these skills far more convincingly than the list alone.
Networking Skills for Cybersecurity in 2026
Networking fundamentals are evolving in implementation, not in underlying substance. Cloud computing has shifted much of enterprise networking into API-driven, software-defined environments. Zero Trust architecture assumes no user or device is automatically trusted, even inside a traditional network perimeter, which changes how segmentation and access control get designed. Hybrid infrastructure — combining on-premises and cloud — requires fluency across both. Containers and Kubernetes introduce their own networking layer on top of traditional infrastructure. SaaS adoption means a growing share of organizational traffic never touches infrastructure the organization directly controls at all. Remote work has pushed more traffic through VPNs and cloud gateways rather than a single physical office network. Network detection and response (NDR) tools increasingly apply advanced analytics to traffic patterns. AI-assisted security monitoring is helping triage the growing volume of network telemetry faster than manual review alone ever could.
None of this changes the underlying fundamentals — TCP/IP, DNS, routing, and firewalls still work the way they always have. What’s changed is where that knowledge gets applied, and building it on durable fundamentals rather than chasing whichever platform is trending is what actually holds up over a career.
Frequently Asked Questions
Do I need networking to learn cybersecurity?
Yes. Nearly every meaningful security event involves network communication in some form, and understanding networking is what lets a security professional interpret what’s actually happening rather than just reading a tool’s summary.
How much networking should a beginner know?
Enough to comfortably explain IP addressing, ports and protocols, DNS, and basic packet flow — depth beyond that can build gradually as a career progresses.
Is subnetting necessary for cybersecurity?
Yes, at least at a working level. Subnetting underlies segmentation, firewall rule design, and a meaningful share of incident investigation reasoning.
Should I learn networking before penetration testing?
Yes. Enumeration — one of the core early stages of any penetration test — is almost entirely a networking skill, and attempting to learn offensive tools without this foundation tends to produce shallow, tutorial-dependent capability.
Is TCP/IP important for SOC analysts?
Very. Reading and correctly interpreting SIEM alerts, firewall logs, and network-based detections all depend directly on understanding how TCP/IP actually works.
Which networking commands should cybersecurity beginners learn?
ping, ip addr, ip route, ss, traceroute, dig, curl, and tcpdump form a solid, practical starting set.
Is Wireshark difficult to learn?
The interface can feel dense at first, but the underlying concepts — the same protocols and packet structures covered throughout this guide — are what actually make it usable. Comfort builds quickly with regular, hands-on practice.
What is the difference between TCP and UDP?
TCP is connection-oriented and reliable, guaranteeing ordered delivery; UDP is connectionless and faster, with no delivery guarantee, making it suited to latency-sensitive traffic like DNS and streaming.
Why is DNS important in cybersecurity?
DNS activity reveals a huge amount about what a system is actually communicating with, making it one of the most valuable and accessible signals for detecting malicious activity, investigating domains, and tracking threat intelligence.
Do cloud security professionals need networking?
Yes, arguably more than ever — cloud networking implements the same underlying concepts (subnets, routing, firewalls) through a provider’s specific tooling, and a shaky networking foundation makes cloud security work significantly harder to reason about correctly.
How long does it take to learn networking for cybersecurity?
There’s no fixed timeline, but a few months of consistent, hands-on study covering the concepts in this guide is a reasonable expectation for solid working fundamentals, with depth continuing to build over a career.

Leave a Reply