

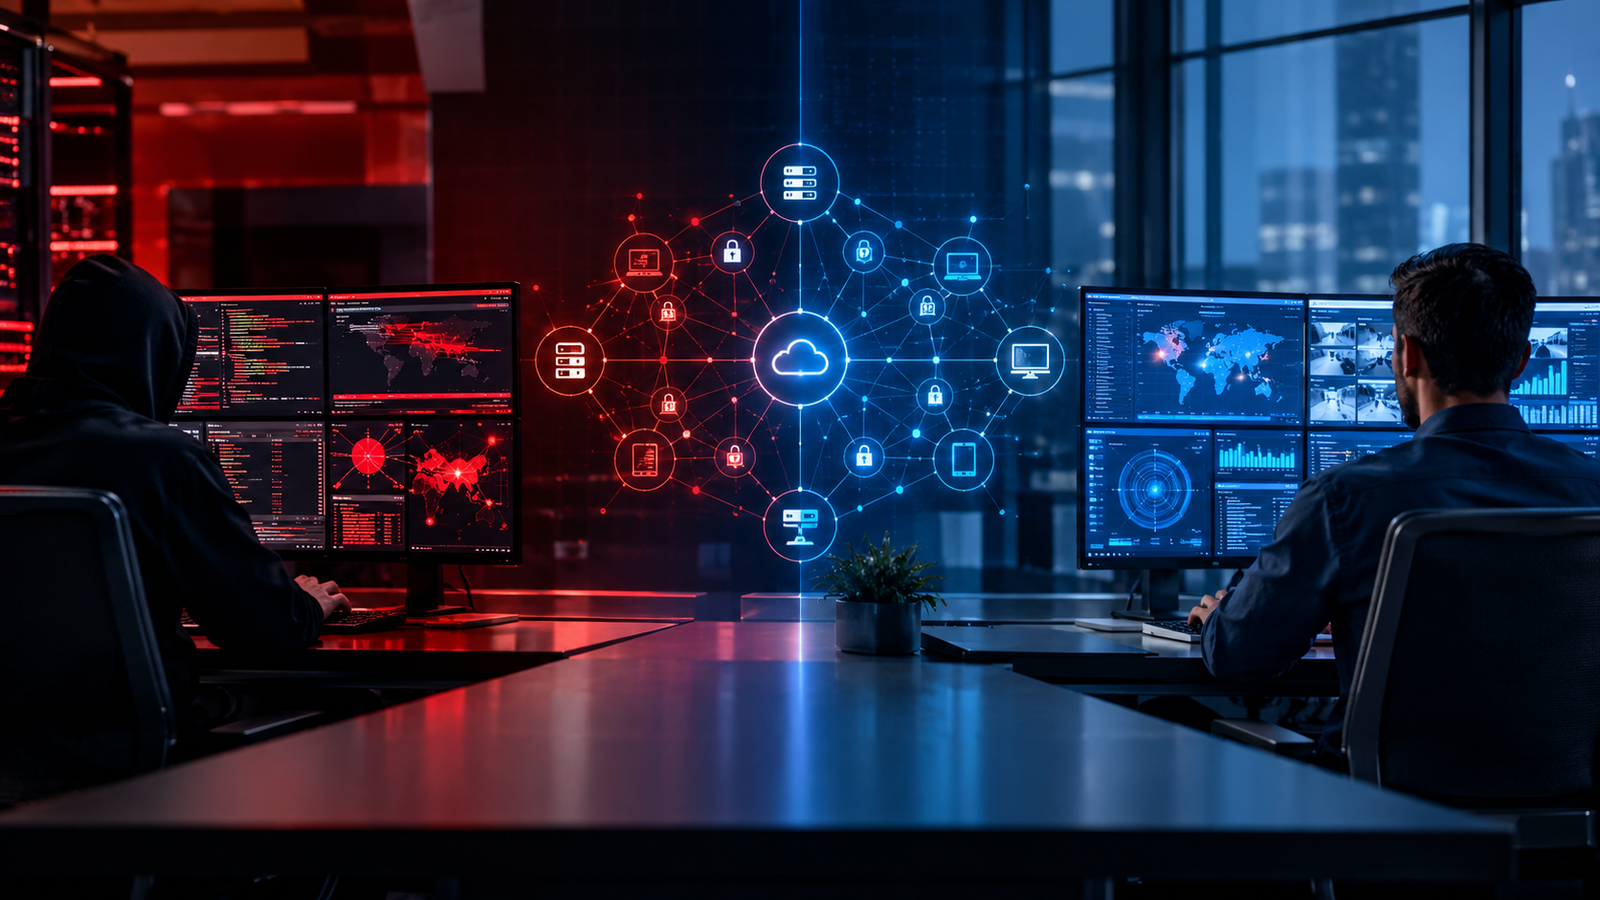
What Is Red Teaming?
Red Teaming is an authorized, objective-based security exercise in which a team simulates the tactics, techniques, and procedures of real-world adversaries to test whether an organization can detect, withstand, and respond to a genuine attack — not just whether a single system has a patchable flaw.
That last distinction matters more than most beginners realize. A vulnerability scan tells you a door is unlocked. A Red Team engagement tells you whether anyone would notice if someone walked through it, moved through the building, and reached the server room. Red Teaming isn’t about finding as many bugs as possible; it’s about proving — or disproving — an organization’s overall resilience against a motivated attacker chasing a specific business-critical objective, such as accessing customer financial data, compromising a domain controller, or exfiltrating intellectual property.
Organizations run Red Team exercises for a few concrete reasons: to validate that expensive security controls actually work under pressure, to test whether the Security Operations Center (SOC) can detect and respond to a live intrusion, to surface attack paths that automated scanners can’t see (the kind that chain together a misconfigured share, a weak service account, and an overprivileged group membership), and to give leadership an honest, evidence-based picture of risk instead of a checklist of “compliant” boxes.
None of this happens without written authorization. Every legitimate Red Team engagement starts with a signed scope, defined rules of engagement, and explicit permission from the organization being tested. Testing systems without authorization isn’t Red Teaming — it’s a crime, regardless of intent. Publications like ValuFlash regularly track how these engagements play out across real organizations, and the patterns tend to repeat: authorization and scope discipline separate legitimate security work from everything else.
What Is Blue Teaming?
Blue Teaming is the defensive discipline of protecting an organization’s systems, data, and people — through continuous monitoring, threat detection, incident response, threat hunting, vulnerability management, and security hardening, all aimed at reducing the time it takes to detect and stop an attacker.
Calling Blue Teamers “the people who defend against hackers” undersells the job badly. A modern Blue Team is closer to an air-traffic-control-and-emergency-response hybrid: they’re watching a constant stream of telemetry from endpoints, networks, cloud environments, and identity systems (monitoring); they’re building and tuning the logic that separates a real threat from background noise (detection engineering); they’re proactively searching for adversaries who evaded automated alerts (threat hunting); they’re the ones who get paged at 2 a.m. to contain a live incident before it spreads (incident response); and they’re the ones closing the gaps attackers would otherwise walk through in the first place — patching, segmenting networks, tightening identity controls, and fixing misconfigurations (hardening and vulnerability management).
A strong Blue Team doesn’t just react to alerts. It shapes the environment so there are fewer things to react to, and it gets faster and sharper every time an incident — real or simulated — reveals a gap in coverage.
Red Teaming vs Blue Teaming: The Core Difference
The simplest way to frame red team vs blue team is this: Red Teams simulate the attack, Blue Teams defend against it — and the value of the exercise comes from what happens when the two collide.
| Area | Red Team | Blue Team |
|---|---|---|
| Primary goal | Prove whether a realistic attacker could reach a specific objective undetected | Detect, contain, and stop attacks as early as possible |
| Security approach | Offensive — think like an adversary | Defensive — think like a protector and investigator |
| Main activities | Reconnaissance, exploitation, privilege escalation, lateral movement, objective achievement | Monitoring, detection, threat hunting, incident response, hardening |
| Typical tools | Nmap, Burp Suite, Metasploit, Cobalt Strike, BloodHound, Impacket | SIEM, EDR/XDR, IDS/IPS, SOAR, threat intel platforms |
| Key skills | Networking, Active Directory, web/API security, scripting, adversary tradecraft | Log analysis, detection engineering, forensics, incident handling |
| Deliverables | Attack narrative, proof-of-concept exploitation, business-impact report | Detection rules, incident reports, hardening recommendations |
| Success measurement | Objectives achieved, attack paths found, stealth maintained | Mean time to detect/respond, detection coverage, containment speed |
| Career roles | Penetration Tester, Red Team Operator, Adversary Simulation Specialist | SOC Analyst, Incident Responder, Detection Engineer, Threat Hunter |
In plain language: Red Teams answer “could an attacker actually get in and reach something that matters?” Blue Teams answer “would we notice, and how fast could we stop it?” Neither question is meaningful without the other — a Red Team finding is only useful if it drives a Blue Team improvement, and a Blue Team’s confidence is only real if it’s been tested by someone trying to break it.
Offensive Security vs Defensive Security
Offensive Security
Offensive security is the umbrella discipline that includes adversary simulation, penetration testing, exploitation research, and attack-path mapping. Its job is to actively attempt to break things — legally and with permission — so the organization learns where it’s actually exposed rather than where it assumes it’s exposed. Red Team operations sit at the mature end of this spectrum: broader in scope, longer in duration, and more focused on business objectives than any single vulnerability.
Defensive Security
Defensive security covers detection, prevention, monitoring, threat hunting, incident response, and security engineering — the work of building and operating the systems that catch and stop what offensive security is designed to find. It’s less about a single event and more about sustained operational readiness: is the environment watched, are the right alerts firing, and does the team know what to do when one does?
Modern cybersecurity needs both sides working together. Defense without offense tends to become theoretical — controls that look good on paper but have never been pressure-tested. Offense without defense becomes an academic exercise — findings that pile up in a report nobody acts on. The organizations with genuinely strong security postures treat offensive and defensive security as two halves of the same continuous improvement loop, not two separate departments that happen to share a budget line.
What Does a Red Team Actually Do?
Planning and Rules of Engagement
Every engagement begins here. The team and the client agree on scope (which systems, networks, and applications are in play), objectives (what “success” looks like — domain admin, access to a specific database, physical access to a data center), testing windows, explicit safety boundaries (systems that are off-limits, actions that require a stop-and-check), and a communication plan for emergencies. This document is the legal and ethical foundation of the entire exercise — nothing happens without it.
Reconnaissance
The team maps the organization’s attack surface using passive techniques (public records, DNS data, employee information, leaked credentials) and, where authorized, active techniques (scanning, service enumeration) to understand what’s exposed and where the likely entry points are.
Initial Access
This is the stage where the team attempts to gain an initial foothold in the environment — commonly through a phishing simulation, an exposed application, or a misconfigured external service, depending on what’s in scope. The specific tradecraft here is sensitive by nature; the goal for a reader is understanding that this step exists and is tightly bound by the rules of engagement, not learning how to execute it against real systems.
Privilege Escalation
Once inside, attackers rarely start with the access they need. Privilege escalation is the process of moving from a low-privilege foothold toward higher-value permissions — because most valuable objectives (databases, domain controllers, financial systems) require elevated access that the initial entry point doesn’t provide.
Lateral Movement
A single compromised laptop is rarely the objective. Lateral movement is how an attacker expands from one compromised asset to others across the network, often revealing additional attack paths that weren’t visible from the outside — which is exactly why internal segmentation and monitoring matter so much.
Persistence
Persistence refers to the techniques attackers use to maintain access to an environment over time, even if their original entry point is closed. Understanding that this concept exists — and that it’s a key thing Blue Teams must detect — is more important here than any specific mechanism, which is why operational detail is intentionally left out.
Objective Achievement
This is where the engagement is measured against its original goal. Did the team reach the agreed objective — access to a specific data set, control of a specific system — while demonstrating a realistic, reproducible path an actual adversary could take? Objective achievement (or a documented near-miss) is the core evidence the rest of the engagement is built around.
Reporting
The final and arguably most valuable deliverable. A strong Red Team report tells the full attack narrative in a way non-technical executives and technical defenders can both use: the attack paths taken, the findings and evidence behind each step, the business impact if a real adversary had done this, the specific defensive gaps that allowed it, and prioritized recommendations. A Red Team engagement that ends without a clear, actionable report has wasted everyone’s time.
What Does a Blue Team Actually Do?
Security Monitoring
Blue Teams watch a constant stream of data — SIEM alerts, raw logs, endpoint telemetry, and network telemetry — to build a real-time picture of what’s happening across the environment. Monitoring is the foundation everything else in defensive security is built on; you can’t detect what you’re not watching.
Threat Detection
This is the discipline of turning raw telemetry into meaningful signal: recognizing indicators of compromise, writing and tuning detection rules, and identifying behavioral patterns and suspicious activity that don’t match a known “good” baseline.
Threat Hunting
Not every intrusion trips an alert. Threat hunting is the proactive, hypothesis-driven search for adversary activity that automated detection missed — analysts actively looking for the needle instead of waiting for the haystack to catch fire.
Incident Response
When something real is found, incident response is the structured process that follows: detection, triage (how serious is this, really?), containment (stop it from spreading), eradication (remove the adversary’s access), recovery (return to normal operations), and lessons learned (make sure it’s harder next time).
Security Hardening
Hardening is the preventive side of the job — tightening identity controls, securing endpoints, segmenting networks, managing patches, and fixing insecure configurations before an attacker ever gets a chance to exploit them.
Vulnerability Management
This is the ongoing cycle of discovering vulnerabilities across the environment, prioritizing them by actual risk (not just severity score), driving remediation, and validating that fixes actually worked. It’s less glamorous than incident response but arguably prevents more incidents than any single detection rule.
Red Team Tools
Red Team tooling generally falls into a few categories: reconnaissance and scanning (Nmap for network and service discovery), web application testing (Burp Suite for intercepting and manipulating web traffic to find flaws like injection or broken access control), exploitation frameworks (Metasploit for testing known vulnerabilities in a controlled way), adversary simulation platforms (Cobalt Strike, widely used for command-and-control and post-exploitation simulation in professional engagements), Active Directory attack-path mapping (BloodHound, which visualizes privilege relationships across a Windows domain so testers — and defenders — can see realistic escalation routes), traffic analysis (Wireshark for packet-level inspection), Windows protocol tooling (Impacket, a Python library used for interacting with Windows network protocols during authorized testing), and full operating environments purpose-built for this work (Kali Linux, a Linux distribution preloaded with security testing tools).
It’s worth saying plainly: these tools don’t replace security knowledge, they extend it. Handing an intercepting proxy or an exploitation framework to someone who doesn’t understand the underlying protocol, network, or authorization boundary just produces noise — or legal exposure. The tool executes; the operator has to know why.
Blue Team Tools
Defensive tooling is organized around visibility and response speed. A SIEM (Security Information and Event Management platform) aggregates and correlates logs across the environment; EDR/XDR (Endpoint/Extended Detection and Response) tools watch endpoint behavior in real time and can often contain a compromised device automatically; IDS/IPS systems detect or block malicious network traffic; firewalls control what traffic is allowed in and out of network segments in the first place; vulnerability scanners continuously check systems for known weaknesses; SOAR platforms (Security Orchestration, Automation, and Response) automate repetitive response steps so analysts can focus on judgment calls; threat intelligence platforms feed context about active adversary campaigns into detection logic; and dedicated network monitoring and log management systems keep the raw data organized and searchable.
Common enterprise examples include Microsoft Sentinel and Splunk for SIEM, CrowdStrike for EDR, and Wazuh or Elastic Security as open-source-friendly monitoring options — though the specific product landscape shifts constantly, so it’s worth checking a platform’s current capabilities before committing to it.
Red Team Skills vs Blue Team Skills
Red Team Skills
Strong Red Team operators build on solid networking fundamentals, comfort in both Linux and Windows environments, a working understanding of Active Directory, web and API security concepts, scripting or programming ability (Python and PowerShell are common), a research mindset for finding and understanding new vulnerabilities, an understanding of realistic adversary simulation, basic operational security (OPSEC) awareness, and — critically — the ability to write a report a non-technical executive can act on.
Blue Team Skills
Strong Blue Team analysts need the same networking foundation, Windows and Linux administration experience, SIEM proficiency, sharp log-analysis instincts, detection-engineering skills (writing and tuning the rules that actually catch things), threat-hunting methodology, structured incident-response process, digital forensics basics, endpoint and cloud security knowledge, and clear reporting ability.
The overlap is bigger than most beginners expect: networking, operating systems, and clear technical writing sit underneath both career paths. That’s part of why moving between Red and Blue later in a career is common rather than rare — the fundamentals transfer.
Red Team vs Penetration Testing
This distinction trips up a lot of people entering the field, and it’s worth being precise about it: Red Teaming is not simply “advanced penetration testing.” They’re related but structurally different.
A penetration test typically has a defined, narrower scope (a specific application, network segment, or system), a shorter duration, and an explicit goal of finding and validating as many exploitable vulnerabilities as possible within that scope. It usually isn’t concerned with stealth — the tester is often expected to be noisy so the organization gets a complete list of findings.
A Red Team engagement has a broader, objective-based scope, runs longer, and is deliberately stealthy — the point is often to test whether the SOC notices at all, not just whether a vulnerability exists. A penetration test might report “this login form is vulnerable to SQL injection.” A Red Team engagement might report “starting from a phishing email, we reached domain admin in six hours and your SOC never generated an alert” — a fundamentally different kind of finding, because it tests detection and response, not just exploitability. If you want to go deeper on the practitioner side of this, our detailed breakdown of what a penetration tester actually does day to day is a good next read.
What Is Purple Teaming?
Purple Teaming isn’t a third, separate team sitting between Red and Blue — it’s a collaborative approach where Red and Blue work together in real time, rather than the Red Team disappearing for weeks and handing over a report at the end.
The idea exists because the traditional model — Red attacks in isolation, writes a report, Blue reads it later — wastes a lot of the learning that could happen in the moment. In a Purple Team exercise, the Red Team executes a specific technique while the Blue Team watches their detection stack live, and the two sides immediately discuss: did this generate an alert? If not, why not? What would need to change in the detection logic to catch it next time? That tight feedback loop turns Red Team findings into Blue Team detection improvements far faster than a static report ever could, and it’s increasingly how mature security programs validate their controls on an ongoing basis rather than once a year.
Real-World Red Team and Blue Team Example
Consider a mid-sized company running a mix of cloud infrastructure, customer-facing web applications, employee endpoints, an on-premises Active Directory environment, a distributed remote workforce, and a SOC with standard monitoring tools in place.
The engagement plays out like this: the Red Team identifies an attack path starting from a public-facing application with a subtle misconfiguration. They perform authorized testing and use that foothold to pivot toward internal systems. The Blue Team’s monitoring picks up some of this activity — an unusual authentication pattern triggers an alert — but a later stage, where the Red Team moves laterally using a legitimate but overprivileged service account, goes undetected because no rule was tuned to flag that specific behavior.
Afterward, both teams sit down together and reconstruct exactly what happened, step by step. The gap gets named precisely: the detection stack had visibility into authentication anomalies but not into unusual service-account behavior. Detection rules get rebuilt to cover that gap, the overprivileged account gets scoped down as part of hardening, and weeks later the Red Team retests the same path. This time, the Blue Team catches it early — and the organization now has concrete, measured evidence that its defenses actually improved, not just a promise that they did.
How Red and Blue Teams Work Together
The healthiest version of this relationship follows a repeatable cycle: Plan → Simulate → Detect → Investigate → Improve → Retest.
That means clear communication before, during, and after every exercise; genuine detection validation rather than assumption; security controls tested under realistic pressure instead of only audited on paper; honest lessons-learned sessions that don’t turn into blame; systematic attack-path analysis that feeds directly into detection engineering; and — critically — retesting, so improvements are verified rather than just claimed. Organizations that skip the retest step often repeat the same gaps a year later under a different name.
How Organizations Measure Red Team Success
The number of vulnerabilities found is a weak metric on its own — it says more about how much time was spent looking than how secure the organization actually is. Better measures include: whether the agreed objectives were achieved, how many distinct attack paths were discovered, how much of the environment the detection stack actually covered, mean time to detect (how long the SOC took to notice, if it noticed at all), mean time to respond, how effective specific controls proved to be under real pressure, how completely findings get remediated afterward, and — again — whether a retest confirms the fix actually worked.
How Organizations Measure Blue Team Effectiveness
Meaningful Blue Team metrics look past raw alert volume toward outcomes: detection coverage across the environment, the quality of alerts (a high false-positive rate quietly burns out analysts and buries real threats), mean time to detect, mean time to respond, how completely incidents get contained, how effective proactive threat hunting proves to be, how quickly vulnerabilities actually get remediated, and overall security-control coverage. The distinction that matters most here is between activity metrics (“we closed 400 tickets this month”) and outcome metrics (“we cut detection time for lateral movement from six hours to twelve minutes”) — the second kind is what actually reflects a stronger security posture.
Certifications for Red Team and Blue Team Careers
Red Team / Offensive Security
Common starting points include CompTIA Security+ as a foundational credential, eJPT (eLearnSecurity Junior Penetration Tester) as an accessible entry-level practical certification, PNPT (Practical Network Penetration Tester) for realistic hands-on assessment, and OSCP (OffSec Certified Professional) as one of the most respected hands-on offensive certifications in the industry — a detailed look at whether OSCP is worth pursuing right now is worth reading before committing the time and cost.
Blue Team / Defensive Security
On the defensive side, common paths include Security+ as a shared foundation, CySA+ (CompTIA Cybersecurity Analyst) for detection and analysis fundamentals, BTL1 (Blue Team Level 1) for hands-on SOC-focused skills, and SC-200 (Microsoft Security Operations Analyst) for cloud-and-Microsoft-stack-specific defensive skills.
Certifications open doors and validate a baseline, but hands-on practice — labs, home environments, real detection work — is what actually builds the judgment employers are paying for. Treat certifications as a supplement to practice, not a substitute for it, and always verify a certification’s current requirements and reputation before investing time and money in it.
Red Team Career Path
A typical offensive-security progression moves from Junior Penetration Tester into a full Penetration Tester role, then toward more specialized Red Team Operator or Adversary Simulation Specialist positions, eventually reaching Security Consultant, Red Team Lead, or dedicated Security Researcher roles. Progression is driven less by titles and more by demonstrable skill: a portfolio of documented lab work, consistent time in practice environments, relevant certifications, and — increasingly — a track record of clear, business-relevant reporting, which is often what separates a good tester from a great one.
Blue Team Career Path
Defensive careers commonly start as a SOC Analyst or Security Analyst, move toward Incident Responder or Threat Hunter as investigative skills deepen, and can branch into Detection Engineer or Security Engineer roles focused on building rather than just operating defenses, eventually reaching Security Architect or Blue Team Lead positions. Progression here rewards depth in log analysis and detection logic early on, followed by broader systems and architecture knowledge as the role becomes more senior — a closer look at what a Security Analyst actually does day to day is a useful starting point if this path appeals to you, and understanding what an Incident Responder’s job really involves helps clarify where the role sits relative to a standard SOC analyst position.
Red Team or Blue Team — Which Is Better for Beginners?
Neither side is universally “better” — the right starting point depends on how you think and what keeps you engaged.
Red Team work tends to reward people who enjoy open-ended problem-solving, creative attack-path thinking, and a steeper, more self-directed learning curve involving heavy scripting and exploitation research. Blue Team work tends to reward people who enjoy pattern recognition, investigation, structured process, and the satisfaction of catching something before it becomes a real incident — often with a gentler on-ramp into the field, since SOC analyst roles are typically more accessible entry points than penetration testing roles.
Both require solid networking, Linux, and Windows fundamentals, and both offer real career opportunities — including freelancing and consulting potential — so treat this less as a permanent fork and more as “which door do I want to walk through first,” since moving between the two later is entirely normal.
Can Red Teaming Be a Freelancing or Consulting Career?
Yes, legitimately, through services like authorized penetration testing, web application and API security assessments, and broader adversary-simulation consulting for organizations that don’t have in-house Red Team capability. Building this kind of practice means treating the business side as seriously as the technical side: real client acquisition, tightly defined scope for every engagement, written authorization before any testing begins, clear rules of engagement, solid contracts, professional reporting, and — where the client wants it — retesting to confirm fixes worked. None of this guarantees income; like any consulting field, it takes time to build a reputation and a client base. A practical walkthrough of building a cybersecurity freelancing career covers the business mechanics in more depth than this article has room for.
Can Blue Team Skills Be Used for Freelancing?
Also yes, and arguably with more potential for recurring revenue. Services like security monitoring setup, SIEM implementation support, detection engineering, log management, security hardening, incident-response readiness planning, vulnerability management, and periodic security assessments are all things small and mid-sized businesses need but often can’t justify a full-time hire for. Setup and hardening work tends to be project-based, while monitoring, detection tuning, and ongoing vulnerability management naturally lend themselves to retainer relationships — which is often the more sustainable freelancing model on the defensive side.
How to Start Learning Red Teaming
Step 1 — Networking
Understand how traffic actually moves: IP addressing, routing, common protocols, and how to read packet captures.
Step 2 — Linux
Get genuinely comfortable in a Linux shell — most offensive tooling lives here.
Step 3 — Windows and Active Directory
Learn how enterprise Windows environments and domain authentication actually work, since most real-world attack paths run through AD.
Step 4 — Web Security
Study the OWASP Top 10 and practice finding common web application flaws in legal lab environments.
Step 5 — Ethical Hacking Fundamentals
Learn the methodology behind authorized testing — scoping, permission, and the overall attack lifecycle — before touching offensive tools.
Step 6 — Penetration Testing
Practice the full process end to end: recon, exploitation, and reporting, in a lab you own or are explicitly authorized to test.
Step 7 — Red Team Concepts
Layer in objective-based thinking, stealth, and adversary simulation on top of straightforward penetration testing skills.
Step 8 — Labs and CTFs
Build hands-on reps in structured environments designed for this — consistency matters more than any single hard challenge.
Step 9 — Reporting
Practice writing findings the way a real client would need to read them — clear, prioritized, and tied to business impact.
Step 10 — Advanced Specialization
Once the fundamentals are solid, branch into a specialty — cloud attack paths, Active Directory tradecraft, or application security research.
How to Start Learning Blue Teaming
Step 1 — Networking
Same foundation as the offensive side — you can’t detect abnormal traffic if you don’t understand normal traffic.
Step 2 — Operating Systems
Build real administration comfort in both Windows and Linux, since you’ll be investigating both.
Step 3 — Security Fundamentals
Learn core concepts: the CIA triad, common attack techniques, and how organizations structure defense in depth.
Step 4 — Logs and Monitoring
Practice reading raw logs before relying on a dashboard to interpret them for you.
Step 5 — SIEM
Get hands-on with a SIEM platform — building queries and understanding correlation logic is a core SOC skill.
Step 6 — Endpoint Security
Learn how EDR tools work and what normal versus suspicious endpoint behavior actually looks like.
Step 7 — Threat Detection
Study indicators of compromise and practice writing or tuning basic detection rules.
Step 8 — Incident Response
Learn the structured response lifecycle and practice it in tabletop or simulated scenarios.
Step 9 — Threat Hunting
Practice proactive, hypothesis-driven investigation rather than waiting for alerts to tell you where to look.
Step 10 — Detection Engineering
Move from using detection rules to building and refining them — this is where senior defensive careers head.
Best Practice Labs for Red and Blue Teams
Legitimate places to build skill without legal risk include reputable CTF platforms, structured cybersecurity training labs, intentionally vulnerable applications built for practice, local virtual machines you control end to end, dedicated detection-engineering labs, SIEM practice environments, and Blue Team simulation platforms built around realistic incident scenarios. The one rule that overrides everything else: only test systems you own or have explicit written permission to test — full stop, no exceptions.
Common Mistakes Beginners Make
The most common missteps include jumping straight to tools before learning the fundamentals underneath them, assuming Red Teaming means “hacking anything you want,” skipping networking basics, ignoring Windows and Active Directory in favor of only Linux, overlooking logs and detection entirely, only ever following CTF walkthroughs instead of solving independently, collecting certifications without matching hands-on practice, never practicing reporting until it’s needed on the job, testing systems without authorization, and treating automated tools as a substitute for actual security expertise rather than an extension of it.
The Future of Red Teaming and Blue Teaming
AI is already reshaping both sides of this field. On the defensive side, AI-assisted detection and automated triage are helping SOC teams handle rising alert volume without proportional headcount growth. On the offensive side, “AI red teaming” — testing AI systems and large language models themselves for security weaknesses — is becoming its own emerging specialty, alongside the more established growth areas of cloud security, identity security, API security, and SaaS security. Continuous security validation and detection engineering are increasingly replacing the old model of a single annual assessment, moving toward ongoing testing and tuning.
None of this replaces human judgment. Authorization decisions, business context, and the nuanced call of “is this actually a threat” still require a person accountable for the outcome — AI is changing the workflow, not the fundamental need for skilled Red and Blue Team professionals who understand both the technology and the organization it’s protecting.
Frequently Asked Questions
What is Red Teaming? Red Teaming is an authorized exercise where a team simulates real-world adversary behavior to test an organization’s overall security resilience against a specific objective, not just individual vulnerabilities.
What is Blue Teaming? Blue Teaming is the defensive discipline of monitoring, detecting, and responding to threats, along with the ongoing work of hardening systems to reduce what attackers can exploit in the first place.
What is the difference between Red Team and Blue Team? Red Teams simulate attacks to test defenses; Blue Teams operate and improve those defenses. One tests, the other protects — and both need each other to be effective.
Is Red Teaming offensive security? Yes — Red Teaming sits within the broader offensive security discipline, alongside penetration testing and exploitation research.
Is Blue Teaming defensive security? Yes — it covers detection, monitoring, incident response, and the preventive work of hardening an environment.
Is penetration testing the same as Red Teaming? No. Penetration testing is typically narrower in scope and focused on finding vulnerabilities; Red Teaming is broader, objective-based, and deliberately tests detection and response, not just exploitability.
What is Purple Teaming? Purple Teaming is a collaborative approach where Red and Blue Teams work together in real time, turning attack simulation directly into detection improvement rather than waiting for a final report.
Which is harder, Red Team or Blue Team? Neither is objectively harder — they demand different kinds of difficulty. Red Team work leans on creative, open-ended problem-solving; Blue Team work leans on sustained investigative discipline and pattern recognition.
Which is better for beginners? It depends on how you think. Blue Team roles often have a gentler entry point; Red Team roles reward people drawn to exploitation and creative attack-path thinking from the start.
What tools do Red Teams use? Common tools include Nmap, Burp Suite, Metasploit, Cobalt Strike, BloodHound, Wireshark, Impacket, and Kali Linux as a testing platform.
What tools do Blue Teams use? Common tools include SIEM platforms, EDR/XDR, IDS/IPS, firewalls, vulnerability scanners, SOAR platforms, and threat intelligence feeds.
Do Red Teamers need programming skills? Yes, at least scripting proficiency — Python and PowerShell are common — to automate tasks and understand or adapt existing tooling.
Do Blue Teamers need coding skills? Basic scripting is increasingly valuable for automation and detection engineering, though it’s less central than for Red Team work.
Can Red Teamers freelance? Yes, through authorized penetration testing and adversary simulation consulting, provided the business fundamentals — contracts, scope, authorization — are handled properly.
Can Blue Teamers freelance? Yes, particularly through monitoring setup, detection engineering, hardening, and ongoing security assessment services, many of which suit retainer-based work.
Which certifications are useful? On the offensive side, Security+, eJPT, PNPT, and OSCP are widely respected; on the defensive side, Security+, CySA+, BTL1, and SC-200 are common starting points.
Can someone move from Blue Team to Red Team? Yes — understanding how defenses actually work is a real advantage when learning to simulate attacks against them.
Can someone move from Red Team to Blue Team? Yes — knowing how attackers think is directly useful for building detection logic that actually catches them.

Leave a Reply