

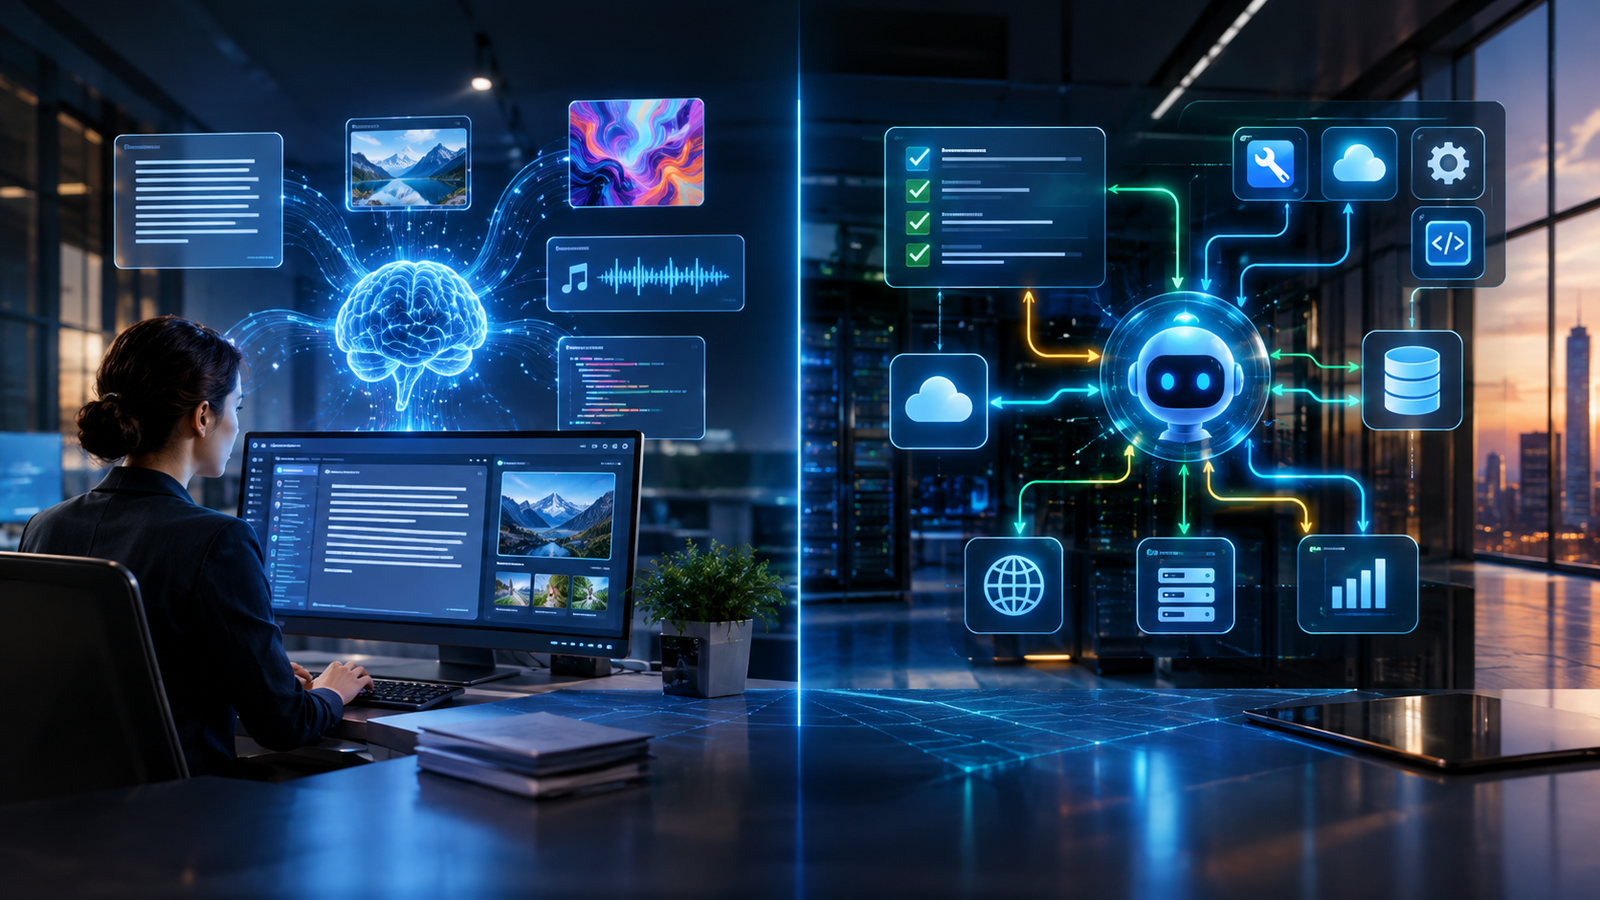
Introduction — Why Agentic AI Is Different From Generative AI
Every wave of software has been defined by what it could do without a human typing the next instruction. Traditional software followed fixed rules. Machine learning added the ability to recognize patterns and make predictions from data. Generative AI went a step further, learning to produce new text, images, code, and audio that looks like it was made by a person. The newest shift — agentic AI — asks a different question entirely: can a system take a goal, figure out the steps to get there, and keep working until the goal is actually met?
That question matters because generating an answer and pursuing an outcome are not the same skill. A generative model can write a polished paragraph about a competitor’s pricing strategy in seconds. It cannot, on its own, decide to go look up that competitor’s current pricing page, cross-reference it against three other sources, notice a contradiction, dig further, and hand back a verified report. The moment a system starts interpreting a goal, planning steps, choosing and using tools, taking actions, checking whether those actions worked, and adjusting course, it has moved into agentic territory.
It’s worth being precise here, because the term gets stretched to cover almost anything with a chat interface. Not every AI agent is fully autonomous, and “agentic” is better understood as a spectrum of behavior than a single, universally agreed-upon architecture. A simple assistant that can call one search tool sits on that spectrum. A system that plans multi-day research projects, coordinates several specialized sub-agents, and only pauses for human approval on high-stakes actions sits much further along it. Both are legitimately “agentic” — they just occupy very different points on the same line.
This article is a practical guide to that spectrum: what generative AI actually does, what agentic AI adds on top of it, how the underlying architecture works, where the real risks live, and how a business or a professional should think about choosing between the two.
What Is Generative AI?
Generative AI refers to AI systems built to create new content — text, images, audio, video, code, or structured data — by learning patterns from large amounts of existing data and then producing original output that follows those patterns.
Rather than sorting inputs into predefined categories the way older machine learning systems did, generative systems learn the underlying structure of the data well enough to produce something new and often convincing on their own. Foundation models — very large models trained on broad datasets — are the backbone of most modern generative AI, and large language models (LLMs) are the specific type behind most text-based generative tools in use today.
It’s worth understanding this distinction at a technical level, not just a marketing one. As one detailed breakdown of discriminative versus generative models explains, the two approaches are trying to answer fundamentally different questions: a discriminative model asks “which category does this belong to,” while a generative model asks “what does this kind of data actually look like, and can I produce more of it.” That underlying mathematical distinction is what makes today’s generative AI systems capable of writing, drawing, and coding rather than just labeling.
How Generative AI Works at a High Level
At a conceptual level, a generative AI interaction follows a simple sequence:
- Input — a person provides a prompt, question, or instruction.
- Context — the model incorporates any additional information available to it: the conversation so far, an uploaded document, or retrieved reference material.
- Model — a neural network, trained on enormous volumes of data, processes that input.
- Inference — the model predicts the most statistically plausible next piece of content, word by word, pixel by pixel, or token by token, depending on the medium.
- Generated output — the final text, image, audio clip, video, or code is produced and returned.
None of this involves the model “deciding” to do anything beyond generating the requested output. It doesn’t check whether the output is correct, take an action based on it, or continue working after the response is delivered unless something external — a person, or another system — prompts it to.
What Generative AI Is Good At
Generative AI genuinely excels at a specific category of work:
- Content generation — drafting articles, marketing copy, product descriptions, and creative writing.
- Summarization — condensing long documents, meetings, or reports into digestible form.
- Translation — converting text between languages while preserving meaning and tone.
- Coding assistance — writing boilerplate code, suggesting fixes, and explaining unfamiliar code.
- Brainstorming — generating a wide range of ideas quickly for a person to evaluate and refine.
- Research assistance — pulling together background information on a topic a person then verifies and builds on.
- Classification and extraction — identifying entities, sentiment, or structured fields within unstructured text.
- Conversational interfaces — powering chatbots and assistants that answer questions in natural language.
Where Generative AI Has Limitations
Generative AI’s strengths come with well-documented limitations that matter for anyone deciding how much to rely on it:
- Hallucinations — a model can generate plausible-sounding but factually incorrect information with the same confident tone it uses for accurate output.
- Limited context — a model can only reason over the information actually provided to it in a given interaction, not everything relevant to a task.
- Lack of guaranteed factuality — nothing in how a generative model works guarantees that its output is true, only that it’s statistically plausible given its training.
- Lack of persistent goals — a generative model responds to the prompt in front of it; it does not independently continue pursuing an objective across sessions unless a surrounding system is built to make that happen.
- Limited external action unless connected to tools — on its own, a generative model can only produce content, not check a database, send an email, or verify a claim against a live source.
- Human oversight requirements — because of the above, generative AI output generally needs human review before it’s used in anything consequential.
What Is Agentic AI?
Agentic AI describes AI systems designed to pursue a goal through multiple steps, typically combining planning, reasoning, tool use, memory or state, observation of results, and iteration until the goal is met or the system determines it cannot proceed further.
Rather than answering a single prompt and stopping, an agentic system treats a request as a goal to work toward. It figures out what steps are needed, decides whether it needs external information or tools to complete those steps, takes action, checks whether that action produced the expected result, and adjusts its approach if it didn’t.
It’s important to describe this accurately rather than dramatically. Agentic AI is not a magical, fully autonomous intelligence that operates without limits. Every agentic system operates within boundaries set by its instructions, the tools it has been given access to, and whatever guardrails and approval steps a developer or business has put in place. What makes a system “agentic” is the presence of a loop — plan, act, observe, adjust — not the absence of constraints.
AI Agent vs Agentic AI
These terms get used loosely, but they describe related, not identical, things:
- AI agent — a single system, usually built around one foundation model, that can perceive input, plan, use tools, and take action toward a defined objective.
- Agentic workflow — a structured sequence of steps, some of which may involve an AI agent making decisions, designed to accomplish a specific business process.
- Agentic system — the broader architecture surrounding one or more agents: the model, the tools, memory, guardrails, and orchestration logic that make the whole thing work reliably.
- Multi-agent system — an architecture in which several specialized agents, each often responsible for a narrower task, coordinate to complete a larger goal.
An AI agent is a component. An agentic system is the whole apparatus built around that component to make it useful, safe, and observable in a real environment. Treating these as perfectly interchangeable terms tends to produce imprecise thinking about what’s actually being built or bought.
How AI Agents Actually Work
Most agentic systems, regardless of the specific framework or vendor behind them, follow a recognizable loop.
Goal
The system receives an objective, either directly from a person or as part of an automated workflow — for example, “research our top three competitors and produce a structured comparison report.”
Planning
The system breaks the goal down into a sequence of smaller steps it believes will accomplish the objective, based on its instructions and the tools it knows are available.
Tool Selection
The agent evaluates whether it can complete the current step using only its own reasoning, or whether it needs to call an external tool — a web search, a database query, a code execution environment, or an internal business API.
Action
The system carries out an authorized action: running the search, querying the database, calling the API, or executing the code.
Observation
The agent receives the result of that action — search results, a database response, an error message, or output from executed code.
Evaluation
The system assesses whether the result actually moves it closer to the goal, or whether something is missing, contradictory, or unusable.
Iteration
Based on that evaluation, the agent either continues to the next planned step, revises its plan and tries a different approach, or determines the task is complete and produces a final result.
A concrete example makes this easier to visualize. Suppose a user asks an AI agent to research competitors and produce a structured report. A single-response chatbot would generate a report immediately, drawing entirely on whatever it already “knows” — with no way to verify that information is current or accurate. An agentic system, by contrast, might work through the task like this:
- Understand the goal and identify what a complete competitor report needs to include.
- Search approved sources for information on each named competitor.
- Gather pricing, feature, and positioning details from those sources.
- Organize the findings into a consistent comparison structure.
- Identify gaps — a competitor whose pricing wasn’t found, a feature list that seems incomplete.
- Perform additional targeted research to fill those gaps.
- Produce a final report, ideally flagging any information it could not verify.
The difference isn’t just “more steps.” It’s the presence of a feedback loop — the system checking its own work and doing something about the gaps it finds — that a single-turn chatbot response simply doesn’t have.
Generative AI vs Agentic AI — The Core Difference
| Capability | Generative AI | Agentic AI |
|---|---|---|
| Generates content | Yes | Yes |
| Follows a prompt | Yes | Yes |
| Multi-step planning | Limited/varies | Core capability |
| Tool use | Possible | Central capability |
| External actions | Usually limited | Often supported |
| Persistent state | Usually limited | Often supported |
| Goal-oriented behavior | Limited | Stronger |
| Feedback loops | Limited | Common |
| Workflow execution | Limited | Strong |
| Autonomy | Usually lower | Can be higher |
| Human oversight | Important | Critical |
A few nuances matter here. Plenty of generative AI products already include some tool use — a chatbot that can search the web or run a calculation is technically using tools, but that doesn’t automatically make it agentic if it isn’t planning multiple steps or iterating based on results. Similarly, not every agentic system operates with high autonomy; many are deliberately built to pause for human approval before taking any consequential action, which is often the more responsible design choice. The table describes tendencies and typical capability profiles, not a strict, universal rule that every product in each category must follow.
Generative AI Is Often the Intelligence Layer — Agentic AI Adds a Workflow Layer
A useful way to think about modern AI systems is as a stack rather than a single product. Foundation models provide the underlying language understanding and generation ability. On top of that sits prompting and instructions that shape how the model behaves. Retrieval systems bring in relevant documents or data. Tools and APIs let the system reach external services. Databases and memory give it state across steps or sessions. Orchestration logic decides what happens when, and business rules and human approval steps constrain what the system is allowed to do on its own.
Generative AI, in this view, is often just the intelligence layer — the part that actually understands language and produces content. Agentic AI is better understood as a system architecture and behavior pattern built around that intelligence layer, not simply a “smarter” or “bigger” language model. A business can plug the same underlying model into a simple chatbot or into a sophisticated multi-step agent; what changes is everything wrapped around it.
Key Components of an Agentic AI System
Understanding agentic AI architecture means understanding what’s actually built around the model.
Foundation Model
At the core sits an LLM or multimodal model responsible for language understanding, reasoning, and content generation. This is the same type of model used in purely generative applications — it’s the surrounding architecture that changes.
Instructions and Goals
Agentic systems need clear system instructions, a defined task objective, and explicit constraints on what the agent is and isn’t permitted to do. Vague instructions tend to produce unpredictable agent behavior.
Memory and State
Agentic systems typically rely on several layers of memory:
- Conversation state — what’s been said or done earlier in the current session.
- Working memory — intermediate findings or partial results relevant to the current task.
- Long-term memory — information retained across sessions, such as user preferences or prior decisions.
- External state — records kept in databases or files outside the model itself.
Memory should never be treated as perfect or permanent. It can be incomplete, outdated, or corrupted, and systems relying on it for important decisions need validation and review, not blind trust.
Tools
Tools are what let an agent act beyond generating text. Common categories include web search, external APIs, databases, code execution environments, file systems, and connections into business software or internal company systems. Standardizing how AI systems connect to these external sources is exactly the problem addressed by the Model Context Protocol, an open standard that gives AI tools a consistent way to reach documentation, databases, and internal systems instead of relying only on frozen training data. Consumer-facing products have gone through a similar evolution — the shift from ChatGPT’s original plugin system to today’s connectors and Custom GPT actions illustrates how quickly tool-use infrastructure for AI systems is maturing.
Planning and Reasoning
Agentic systems break complex tasks into smaller steps, often reasoning about which order to tackle them in and what information each step depends on before it can proceed.
Observability
Businesses deploying agentic systems need real visibility into what the agent is actually doing: which actions it took, which tools it called, what errors occurred, what decisions it made and why, and what those decisions cost in compute, API usage, and latency. Without this, an agent’s behavior becomes a black box that’s difficult to trust or debug.
Guardrails
Guardrails are the constraints that keep an agentic system inside safe operating boundaries: permission boundaries on what data or systems it can touch, restrictions on which tools it can call, requirements for human approval before certain actions, validation of both inputs and outputs, and enforcement of broader business or compliance policy.
AI Agents vs Chatbots
| Factor | Chatbot | AI Agent |
|---|---|---|
| Conversation | Yes | Yes |
| Goal execution | Answers a single prompt | Works toward a defined objective across steps |
| Tool use | Sometimes, per response | Central to completing tasks |
| Memory | Often limited to the current session | Can span sessions and tasks |
| Planning | Minimal or none | Breaks tasks into ordered steps |
| External actions | Rare | Common, within defined permissions |
| Workflow completion | Not designed for multi-step workflows | Designed to carry a workflow to completion |
| Human approval | Reviewed after the fact | Often built into the process itself |
A chatbot is genuinely the right tool when a person needs a quick answer, a draft, or a conversational interaction with no dependency on external systems — answering an HR policy question, drafting an email, or explaining a concept. An agent becomes more appropriate when the task requires several dependent steps, needs to pull from or act on live external systems, or needs to keep working and adjusting until a defined outcome is reached, such as reconciling a batch of invoices against multiple source systems or investigating and triaging a security alert.
Single-Agent vs Multi-Agent Systems
Single-Agent Systems
In a single-agent architecture, one agent is responsible for the entire task — planning, tool use, and execution all happen within one system. This is simpler to build, reason about, and debug, and it’s often the right starting point for most business use cases.
Multi-Agent Systems
A multi-agent architecture splits a larger task across multiple specialized agents that coordinate with each other — for example, a research agent that gathers information, a coding agent that implements a solution, a testing agent that verifies it works, a data analysis agent that interprets results, and a review agent that checks the combined output before it’s finalized.
Multi-agent systems can bring real benefits: specialization tends to improve quality on narrow sub-tasks, and parallel work can speed up complex projects. But they also introduce real problems. Coordinating multiple agents adds architectural complexity. Running several agents, each potentially making multiple model calls, increases cost and latency. Errors made by one agent can propagate into the work of another before anyone notices. And debugging a multi-agent failure — figuring out which agent introduced the problem and why — is meaningfully harder than debugging a single system. Multi-agent architectures aren’t automatically better; they’re a trade-off that makes sense for genuinely complex, decomposable tasks and adds unnecessary overhead for simpler ones.
Real-World Agentic AI Use Cases
Customer Support
Agents can understand a customer’s request, retrieve relevant account information, search internal knowledge bases, draft a response, and escalate genuinely complex issues to a human representative rather than attempting to resolve everything automatically.
Software Development
Agentic tools increasingly assist with code generation, repository analysis, automated testing, debugging support, documentation, and issue triage. Human code review remains essential — an agent that can write and test code is not the same as one qualified to make architectural or security trade-off decisions unsupervised.
Data Analysis
Agents can query databases, clean messy datasets, run statistical analysis, generate charts, and explain findings in plain language, compressing work that used to require manual back-and-forth between an analyst and a dataset.
Marketing
Marketing use cases include research, campaign planning, structured content workflows, and performance analysis across channels. It’s worth noting that agentic behavior is starting to matter for marketing in a second, less obvious way too — AI agents acting on behalf of customers are becoming an audience of their own, which changes what “good” marketing content even looks like when the reader is a system rather than a person.
Finance
In finance, agentic workflows support reporting, reconciliation, document processing, and financial analysis assistance. High-risk financial decisions — capital allocation, credit approval, large transaction authorization — require appropriate human controls and should not be delegated to an autonomous agent without them.
Cybersecurity
Security teams are using agentic systems for alert triage, threat intelligence research, log analysis, and investigation assistance. Given the sensitivity of the systems involved, authorization boundaries, safety constraints, and human oversight are not optional extras here — they’re core requirements.
Agentic AI in Business Operations
The real value of agentic AI in an enterprise setting often comes from connecting multiple existing systems rather than from any single model capability. A realistic workflow might look like: a customer request comes in, the agent checks the CRM for account context, searches the knowledge base for relevant policy, calls an internal API to pull order status, analyzes the combined information, routes the case for human approval if it crosses a risk threshold, takes the approved action, and sends the customer an update.
This is why integration and workflow design frequently matter more to real business outcomes than which specific foundation model sits at the center of the system. A brilliant model wired into a poorly designed workflow will still produce a poor result.
Agentic AI vs Traditional Automation
Rule-based automation and agentic AI workflows solve overlapping but distinct problems.
| Factor | Rule-Based Automation | Agentic AI Workflow |
|---|---|---|
| Logic | Deterministic, explicitly programmed rules | Dynamic reasoning based on context |
| Inputs | Usually structured | Can handle natural language and unstructured input |
| Adaptability | Low — breaks when conditions change unexpectedly | Higher — can adjust its approach mid-task |
| Predictability | Very high | Lower, though improving with guardrails |
| Governance | Simpler to audit and certify | Requires more active oversight |
Traditional automation is often the better choice for high-volume, well-defined, low-variance processes where predictability and auditability matter more than flexibility — payroll processing, standard invoice matching, or regulatory reporting with fixed formats. Agentic AI earns its complexity when a task genuinely requires interpreting varied natural language input, making context-dependent judgment calls, or adapting to situations that don’t fit a fixed rule set.
Agentic AI vs RAG
Retrieval-Augmented Generation (RAG) is a technique, not an architecture pattern in the same sense as “agentic.” RAG retrieves relevant documents or data and feeds them into a model’s context so it can generate a response grounded in that material, rather than relying solely on what it learned during training.
RAG does not automatically make a system agentic. A chatbot that retrieves a policy document and summarizes it in a single response is using RAG, but it isn’t planning multiple steps, using tools beyond retrieval, or iterating based on results. RAG becomes one component inside an agentic system when an agent decides, as part of a broader plan, that it needs to retrieve specific information, evaluates whether what it retrieved is sufficient, and takes further action based on that evaluation. The distinction matters for technical teams evaluating vendor claims: “RAG-powered” and “agentic” describe different things, even though the two frequently appear together in the same product.
Benefits of Agentic AI
- Automation of genuinely multi-step work that previously required manual coordination across systems.
- Reduced manual effort on repetitive research, data-gathering, and reconciliation tasks.
- Faster research turnaround when an agent can search, verify, and synthesize across multiple sources.
- Workflow orchestration that connects previously siloed systems and processes.
- The potential for execution outside standard business hours, within defined guardrails.
- Cross-system integration that reduces manual data re-entry between tools.
- More personalized workflows that adapt to specific user or customer context.
- Scalable digital operations that don’t require linear headcount growth for linear task growth.
These are genuine, well-supported benefits — but they depend heavily on good implementation. An agentic system layered onto a messy, undocumented process tends to automate the mess faster rather than fix it.
Limitations and Risks of Agentic AI
An agent capable of taking real actions can create larger consequences than a system that only generates text, because a bad decision doesn’t stay contained to a document someone reviews before acting on it — it can directly touch a database, a customer, or a live system. This section deserves the weight it gets.
Hallucinations
Agentic systems inherit the same hallucination risk as the generative models underneath them — and because an agent can act on a hallucinated “fact” rather than just stating it, the consequences can compound.
Incorrect Tool Calls
An agent can call the right tool with the wrong parameters, or the wrong tool entirely, producing errors that aren’t always obvious from the output alone.
Excessive Autonomy
Giving an agent more permission, scope, or ability to act without approval than a task actually requires creates an exploitable and error-prone attack surface. Industry security researchers have flagged this specifically: within the OWASP GenAI Security Project’s widely referenced risk framework for large language model applications, “excessive agency” has risen sharply in recent rankings, reflecting how much more consequential this risk becomes as systems gain the ability to act rather than just respond.
Data Leakage
An agent with broad access to internal systems can inadvertently surface sensitive information in a response, log, or downstream action if access controls aren’t scoped tightly.
Prompt Injection
Malicious or manipulated content — embedded in a webpage, document, or email an agent processes — can attempt to override its original instructions. OWASP’s agentic-specific risk taxonomy names this pattern directly as one of the top risks facing autonomous systems, since an agent that treats retrieved content as instructions rather than data can be redirected toward unintended goals.
Excessive Permissions
Related to excessive autonomy, this is specifically about credential and access scope — an agent inheriting broader system permissions than the task in front of it requires.
Cost and Token Usage
Multi-step reasoning, tool calls, and especially multi-agent coordination can consume significantly more compute and API usage than a single generative response, and costs can scale unpredictably with task complexity.
Latency
Each planning step, tool call, and evaluation cycle adds time. Tasks that a person expects to complete quickly may take noticeably longer when handled by a multi-step agent.
Error Propagation
In multi-step or multi-agent workflows, an early mistake can compound as later steps build on a flawed result, sometimes without any single step looking obviously wrong in isolation.
Difficult Debugging
Understanding why an agent made a particular sequence of decisions is harder than debugging a single-response system, particularly across multi-agent workflows with several points of potential failure.
Reliability
Agentic systems, especially newer ones, can behave inconsistently across similar tasks, and reliability tends to be one of the biggest gaps between demo performance and production performance.
Accountability
When an autonomous system takes an action with real consequences, someone still has to be accountable for that outcome. Clear ownership — who approved the agent’s scope, who monitors its behavior, who is responsible when something goes wrong — needs to be established before deployment, not after an incident.
Security Best Practices for Agentic AI
Securing an agentic system means protecting both the model and everything around it — the tools, data connections, and infrastructure it can reach.
- Least privilege — give agents access only to the specific data and systems a task actually requires, nothing broader.
- Tool allowlists — explicitly define which tools an agent can call, rather than granting open-ended access.
- Authentication and authorization — treat every tool connection and data source the same way you would treat any system integration, with proper credential management.
- Human approval for sensitive actions — require explicit sign-off before an agent can take high-consequence actions like financial transactions, data deletion, or customer-facing communications.
- Input validation — treat content an agent retrieves from external sources as untrusted data, not as trusted instructions.
- Output validation — check what an agent produces before it reaches a customer or a downstream system, particularly for actions that can’t easily be undone.
- Sandboxing — run code execution and other risky operations in isolated environments separate from production systems.
- Secret management — never hard-code credentials into agent instructions or expose them in logs the agent can read.
- Logging — keep a detailed record of every action, tool call, and decision an agent makes.
- Monitoring — watch for unusual patterns in agent behavior that might indicate a compromised or malfunctioning system.
- Rate limiting — cap how frequently an agent can call sensitive tools or take consequential actions.
- Data access controls — apply the same governance to what an agent can read and write as you would to a human employee’s access permissions.
- Audit trails — maintain records that make it possible to reconstruct exactly what an agent did and why, after the fact.
Human-in-the-Loop vs Fully Autonomous AI
The right level of autonomy for an agentic system depends on the task, not on a general preference for “more automation.”
Human Approval for Every Action
The agent proposes each step; a human explicitly approves before anything happens. Appropriate for high-risk, high-stakes, or newly deployed systems where trust hasn’t yet been established.
Human Approval for High-Risk Actions
The agent handles low-risk steps independently but pauses for approval on anything consequential or hard to reverse — sending an external communication, modifying financial records, deleting data.
Supervised Automation
The agent executes full workflows independently, with a human monitoring dashboards, logs, and outcomes, intervening when something looks wrong rather than approving every step in advance.
Highly Autonomous Workflows
The agent operates with minimal real-time human involvement, typically reserved for low-risk, well-understood, reversible tasks with a strong track record of reliable performance.
Choosing the right level depends on the risk of the task, how reversible a mistake would be, how sensitive the data involved is, the business impact of an error, and any regulatory requirements that apply. It’s worth resisting the assumption that fully autonomous systems represent an inevitable end state for every use case — for a meaningful share of business processes, some form of human-in-the-loop oversight will remain the appropriate design choice for the foreseeable future, not a temporary limitation waiting to be engineered away.
How to Choose Between Generative AI and Agentic AI
A practical decision framework can be built around a short set of questions:
- Is the task primarily about generating content, with a person reviewing and using the result?
- Does completing the task require multiple dependent steps, not just one response?
- Does the task need external tools, live data, or connections to other systems?
- Does the system need to take real actions, not just produce a recommendation?
- Does the task require remembering state across steps or sessions?
- Is the workflow predictable enough to define clear boundaries and guardrails?
- What’s the realistic cost of an error, and how reversible would it be?
- Can a human meaningfully review the result before it has consequences?
| Signal | Leans Toward Generative AI | Leans Toward Agentic AI |
|---|---|---|
| Task shape | Single-response content creation | Multi-step process with dependencies |
| External data need | Minimal or none | Requires live tools or systems |
| Action required | None — output is reviewed by a person | Yes — the system needs to act |
| Error cost | Low, easily caught in review | Higher, needs guardrails |
| State needed | Little to none | Persistent across steps or sessions |
Many real business needs sit somewhere in between — a good rule of thumb is to start with the simplest architecture that satisfies the requirement, and add planning, tool use, and autonomy only when the task genuinely demands it, rather than defaulting to the more complex option because it’s the more talked-about one.
Skills Needed to Work With Agentic AI
Building agents that actually work requires more than knowing how to write a good prompt.
AI and LLM Fundamentals
Understanding how large language models generate output, their strengths, and their failure modes is the baseline for building anything reliable on top of them.
Prompt Engineering
Clear, well-structured instructions still meaningfully affect how reliably an agent plans and executes tasks.
Python
The dominant language for building, orchestrating, and testing agentic systems in most current tooling ecosystems.
APIs
Agents connect to the world through APIs; understanding how to design, call, and secure them is foundational.
JSON
The common structured format for passing data between models, tools, and systems in agentic workflows.
Databases
Both for retrieving information an agent needs and for storing the state and memory that persist across a task.
RAG
Understanding retrieval architecture — how to fetch relevant, accurate context and feed it into a model reliably.
Tool Calling
Designing and implementing the interfaces that let a model reliably invoke external functions, APIs, or services.
Workflow Automation
Understanding how to structure multi-step business processes so an agent’s actions fit cleanly into existing operations.
Cloud Fundamentals
Most production agentic systems run on cloud infrastructure; understanding deployment, scaling, and cost management matters.
Security
Given the risks outlined earlier, security literacy — access control, sandboxing, input validation — isn’t optional for anyone building agentic systems.
Evaluation and Testing
Knowing how to systematically test an agent’s reliability across varied scenarios, not just check that a demo works once.
Professionals moving into this space are effectively pairing a technical skill set with judgment about when and how much autonomy is appropriate — a combination that’s increasingly recognized as valuable precisely because it can’t be replaced by AI fluency alone. Broader research into which professional skills are becoming more valuable as AI adoption spreads points to the same underlying pattern: execution is being compressed, while judgment, systems thinking, and accountability are becoming more valuable, not less — and agentic AI work sits squarely in that judgment-heavy category.
Technologies Behind Modern Agentic AI
Rather than tying this discussion to any single vendor, it’s more durable to understand the categories of technology involved:
- LLM APIs — the interfaces through which applications access foundation model capabilities.
- Function and tool calling — the mechanisms that let a model request an external action and receive structured results back.
- Agent frameworks — software libraries that provide reusable structure for building planning, memory, and tool-use loops.
- Vector databases — used for semantic search and retrieval in RAG-style architectures.
- Traditional databases — for structured data storage and retrieval that doesn’t require semantic search.
- API integrations — connections to internal business systems and external services.
- Workflow orchestration — tooling that manages the sequence and dependencies of multi-step tasks.
- Observability platforms — tools for logging, monitoring, and debugging agent behavior in production.
- Evaluation systems — frameworks for systematically testing agent reliability before and after deployment.
Specific products in each category change quickly; the underlying categories of capability an agentic system needs are far more stable and worth understanding independent of any particular vendor’s current offering.
How to Build a Simple Agentic AI Project
A beginner-friendly way to understand agentic architecture in practice is to think through a simple AI research assistant.
The basic flow looks like this: a user submits a research question. An agent interprets the goal and decides what information it needs. It calls a search tool to gather relevant sources. It collects and organizes the information it finds. It analyzes that information for gaps, contradictions, or missing detail. It verifies key claims where possible, ideally against more than one source. It produces a final report, noting any information it couldn’t confirm.
The components required to build even this simple version include a foundation model for reasoning and writing, a search tool the agent can call, a way to store intermediate findings as working memory, basic logic for deciding when enough information has been gathered, and a final formatting step to produce a usable report. Even at this small scale, the same architectural pieces — planning, tool use, memory, and evaluation — that show up in enterprise-grade agentic systems are all present. Scaling up mostly adds more tools, more guardrails, and more rigorous testing, not a fundamentally different structure.
Agentic AI Career Opportunities
Several roles are emerging or expanding specifically around building and operating agentic systems:
- AI Engineer — builds and integrates AI capabilities, including agentic workflows, into products.
- AI Application Developer — focuses on the software layer that turns model capability into a usable product.
- AI Automation Engineer — designs and implements agentic workflows that automate business processes.
- Agentic AI Engineer — specializes specifically in multi-step, tool-using agent architecture.
- ML Engineer — works on the underlying model training, fine-tuning, and evaluation infrastructure.
- AI Solutions Architect — designs how AI systems, including agents, fit into broader enterprise architecture.
- AI Product Manager — defines what an AI-powered product, including agentic features, should actually do and for whom.
- AI Security Engineer — focuses specifically on securing AI systems and the tools and data they can access.
These roles overlap considerably in required foundational knowledge — LLM fundamentals, APIs, and basic security awareness show up across nearly all of them — while differing in how much of the job is model-focused engineering versus product judgment versus security-specific depth.
How Agentic AI Could Change Software Development
Software development is already one of the areas most visibly affected by agentic tooling. AI-assisted coding continues to expand beyond autocomplete into more substantial code generation. Autonomous or semi-autonomous testing agents can generate and run test cases against a codebase. Code review assistance can flag issues before a human reviewer even opens a pull request. Documentation generation keeps codebases more maintainable with less manual overhead. Issue management tools can triage and route bug reports. DevOps workflows increasingly incorporate agentic automation for routine deployment and monitoring tasks.
None of this removes the need for software engineering fundamentals. An agent that can generate working code still depends on a human who understands architecture, security implications, and system design well enough to know whether that code is actually the right code for the situation. The tools are changing what a developer spends time on; they aren’t eliminating the underlying judgment the role requires.
The Future of Agentic AI in 2026 and Beyond
It’s worth separating what’s currently working in production from what’s still an emerging or speculative direction.
Currently observable trends include steadily improving tool-use reliability as agent frameworks and underlying models mature, better multi-step reasoning in newer model generations, growing enterprise adoption of agentic workflows for well-scoped, high-value processes, and the emergence of formal security frameworks — including OWASP’s dedicated risk taxonomy for agentic applications — as the industry treats agent-specific security as its own discipline rather than a subset of general LLM security.
Directions that are more genuinely forward-looking, and should be read as reasonable possibilities rather than settled facts, include more capable multimodal agents that can reason across text, images, and other data types within a single workflow; more sophisticated agent-to-agent coordination protocols; stronger, more standardized evaluation practices for measuring agent reliability before deployment; continued development of governance frameworks — building on efforts like the NIST AI Risk Management Framework — specifically addressing autonomous system risk; and growing interest in on-device and edge AI that could eventually support certain agentic capabilities without constant cloud connectivity.
None of this should be read as a guarantee about specific timelines or specific vendors’ roadmaps. The technology, the tooling landscape, and the risk picture are all still moving, and the businesses adopting agentic AI most successfully tend to be the ones treating current capabilities honestly — neither dismissing them as hype nor assuming today’s demo represents a fully solved, risk-free production system.
Frequently Asked Questions
What is Agentic AI? Agentic AI refers to AI systems designed to pursue a goal through multiple steps — planning, using tools, taking actions, and adjusting based on results — rather than simply producing a single response to a prompt.
What is Generative AI? Generative AI refers to AI systems that create new content, such as text, images, audio, video, or code, by learning patterns from data and producing original output that follows those patterns.
What is the difference between Generative AI and Agentic AI? Generative AI focuses on producing content in response to a prompt. Agentic AI focuses on pursuing a goal across multiple steps, often using generative AI as its underlying intelligence layer while adding planning, tool use, memory, and iteration on top of it.
How do AI agents work? Most AI agents follow a loop: they receive a goal, plan a sequence of steps, decide whether external tools are needed, take action, observe the results, evaluate whether the goal has been met, and either continue, adjust their approach, or finish.
Are AI agents the same as chatbots? No. A chatbot typically answers a single prompt in a conversational format. An AI agent is built to complete a multi-step task, often using tools and taking real actions, and continuing until a defined objective is met.
When should businesses use agents instead of generative AI alone? Agents make sense when a task requires multiple dependent steps, needs to pull from or act on live external systems, or needs to keep adjusting its approach until a goal is reached. A single generative AI response is usually sufficient for straightforward content creation reviewed by a person before use.
What are the risks of Agentic AI? Key risks include hallucinations compounding into real actions, incorrect tool calls, excessive autonomy or permissions, data leakage, prompt injection, higher cost and latency from multi-step reasoning, error propagation across steps, difficult debugging, and unclear accountability when something goes wrong.
Conclusion
Generative AI and agentic AI aren’t rival technologies competing for the same job — they’re different layers of the same broader shift toward AI systems that do more than answer questions. Generative AI supplies the language understanding and content-creation ability. Agentic AI wraps that ability in planning, tool use, memory, and iteration so a system can pursue an actual outcome rather than a single response.
The businesses and professionals getting real value from this shift are the ones matching the tool to the task: using generative AI where a good draft reviewed by a person is genuinely enough, and reaching for agentic architecture — with the guardrails, oversight, and security practices it demands — only where a task truly requires multi-step planning and real-world action. Getting that match right, more than picking the most advanced-sounding option available, is what actually determines whether an AI investment pays off. For ongoing coverage of how this landscape keeps evolving, ValuFlash’s AI and technology coverage tracks these shifts as they happen.


Leave a Reply